
Here is your CloudCSF Blog – Day 17 Post
🔐 Control #16: API Gateway Exploits – The Silent Attack Surface
🌐 CloudCSF Day 17
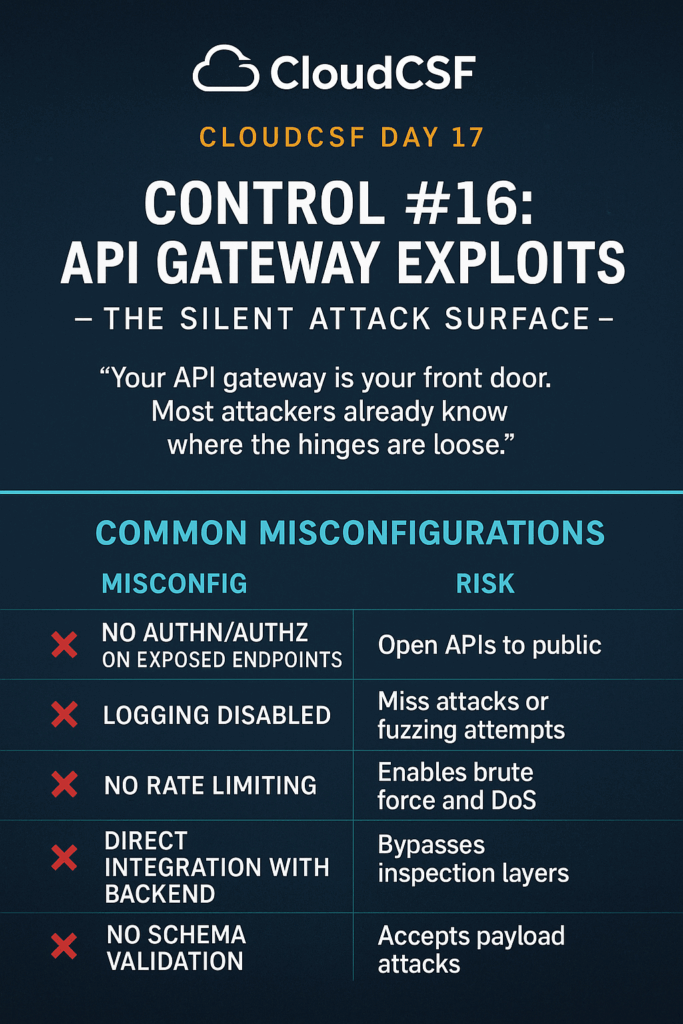
Control #16: API Gateway Exploits – The Silent Attack Surface
“Your API gateway is your front door. Most attackers already know where the hinges are loose.”
🚨 Why This Control Matters
API Gateways (AWS API Gateway, Azure API Management, GCP API Gateway) are powerful – they:
- Expose services
- Route requests
- Handle authentication, rate limits, and logging
But when misconfigured, they:
- Expose backend services
- Bypass authentication if not enforced
- Are rarely tested for security at the gateway level
- Create blind spots in logging and WAF protection
🕳️ Common Misconfigurations
| Misconfig | Risk |
|---|---|
| ❌ No AuthN/AuthZ on exposed endpoints | Open APIs to public |
| ❌ Logging Disabled | Miss attacks or fuzzing attempts |
| ❌ No rate limiting | Enables brute force and DoS |
| ❌ Direct integration with backend | Bypasses inspection layers |
| ❌ No schema validation | Accepts payload attacks |
🔍 CloudCSF API Gateway Exploit Checklist
- Inventory All API Gateway Instances
- Document exposed paths, methods, and integrations
- Enforce Authentication & Authorization
- Use OAuth2/JWT/API Keys
- Test bypass paths and fallback logic
- Enable Logging and Monitoring
- CloudWatch, Stackdriver, Azure Monitor
- Feed into SIEM tools
- Apply Rate Limiting & Throttling
- Set per-client and per-resource limits
- Scan for OWASP API Top 10
- Tools: OWASP ZAP, Burp Suite, Postman Security
- Test for Bypass Paths
/v1/apivs/v1/api/or/v1//api- Encode & Unicode payloads
- Implement WAF in Front
- Layer protection using AWS WAF, Azure Front Door, GCP Armor
- Enforce API Schema Validation
- Use OpenAPI / Swagger specs
- Reject unexpected fields
🔐 Maturity Levels
| Level | Maturity Description |
|---|---|
| ❌ 0 – No Gateway Hardening | Exposed APIs without security layers |
| ⚠️ 1 – Basic Auth Only | No logging or rate limits |
| 🧩 2 – Auth + Logging | No WAF or schema enforcement |
| 🛡️ 3 – Full Hardening | WAF, throttling, validation |
| 🚀 4 – Runtime Protection | Threat detection at API level |
🛠️ Tools to Try
- 🔍 OWASP ZAP – Fuzzing and scanning
- 🔍 42Crunch – API contract testing
- 🔍 Postman + Fuzzers – Input testing
- 🔍 Pynt / Tinfoil / Wallarm – API Security platforms
📘 Bonus Resource
📥 [Download API Gateway Security Audit Checklist (PDF)]
🔗 Join CloudCSF WhatsApp Group for guided API pen testing walkthroughs
💬 Comment :
Have you ever seen an API bypass lead to a production issue?
👇 Comment “APIExposed 🔓” and we’ll send you the checklist!
🔁 Coming Tomorrow:
Day 18: Control #17 – Logging Gaps and the Forensics Fail