
#OneControlAtATime | CloudCSF.com
🌐 CloudCSF Day 31: Unused Cloud Services – The Silent Budget & Risk Killers
#OneControlAtATime | CloudCSF.com
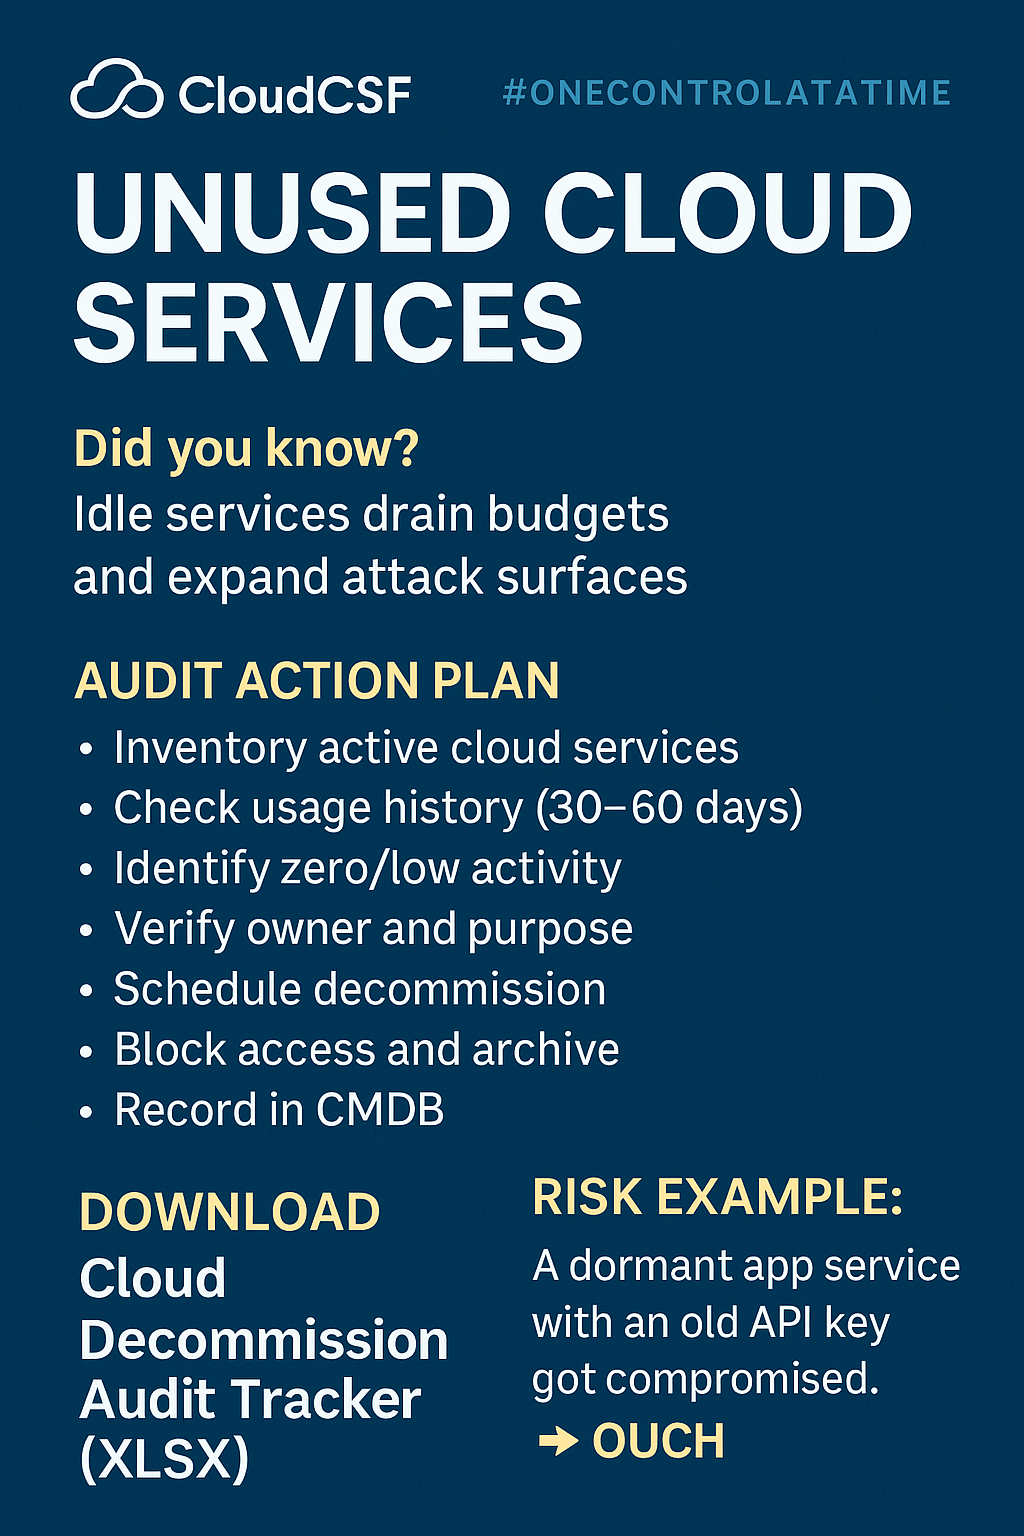
🔍 Did you know?
Many organizations unknowingly keep paying for cloud services they no longer use — and worse, leave them exposed without monitoring or controls.
🎯 Control Focus: Decommissioning Unused Cloud Services
Why it matters:
• Wasted costs from idle services
• Increased attack surface (e.g., open IPs, dormant credentials)
• Outdated configurations often lack logging or MFA
• Forgotten sandbox/test services with production-level access
✅ Audit Action Plan:
🔸 Inventory all active cloud services
🔸 Cross-check usage metrics for last 30–60 days
🔸 Identify services with zero or low activity
🔸 Verify asset ownership, tagging, and purpose
🔸 Schedule decommissioning with approval
🔸 Ensure backup or snapshot is archived before deletion
🔸 Block access + revoke keys or tokens
🔸 Document decommissioning in your CMDB or asset tracker
🛠️ Free Tool:
📥 Download “Cloud Decommission Audit Tracker (XLSX)”
Track, verify, and clean up unused services across AWS, Azure, and GCP.
📌 Real-World Risk Example:
A dormant Azure App Service was exploited because it still had an old API key in a Git repo. It hadn’t been touched in 9 months!
📣 Take Action Now:
You can’t secure what you forget exists.
🔐 Visibility → Ownership → Action = Mature Cloud Security
💬 Comment below with your biggest cloud cleanup win!
🔁 Share this post with your team or community!
#CloudSecurity #CostOptimization #CloudAssetManagement #CloudCSF #AuditSecIntel