
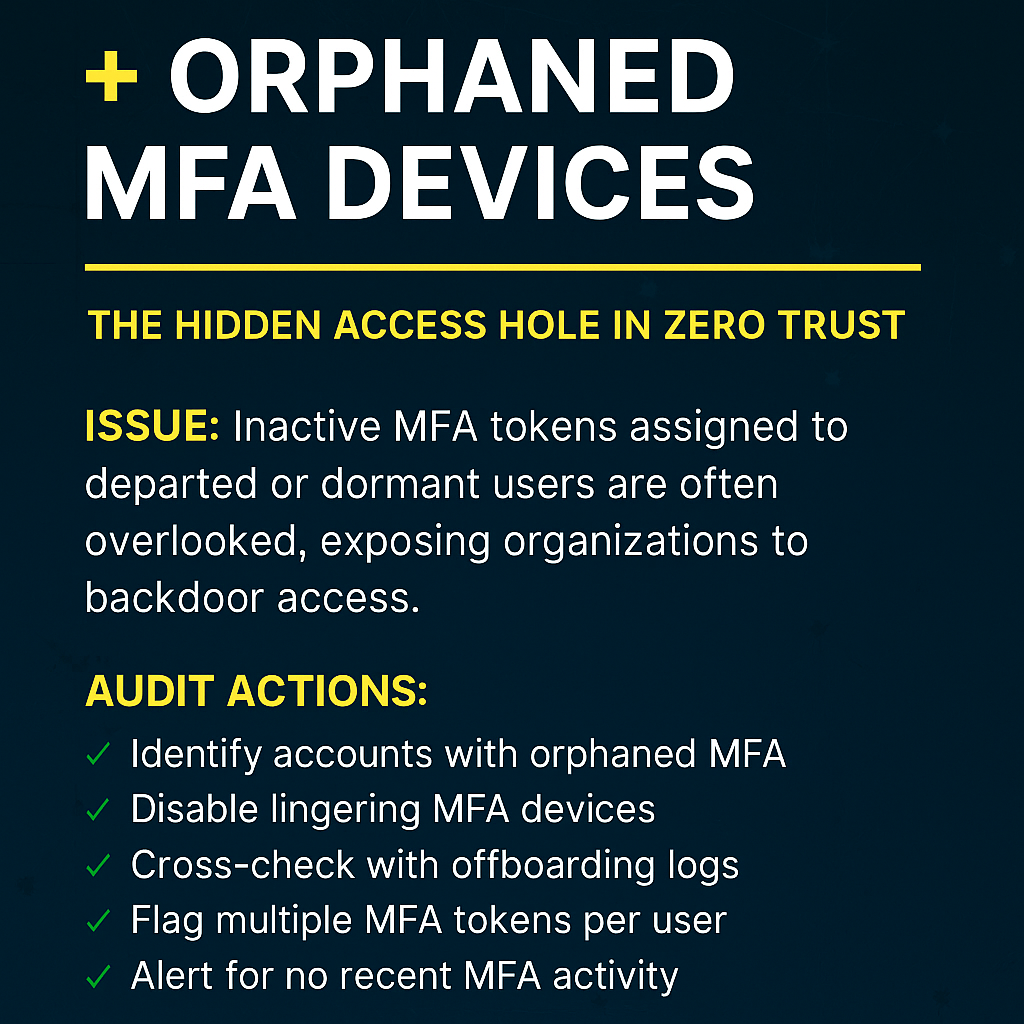
🌐 CloudCSF Day 34: Orphaned Multi-Factor Authentication (MFA) Devices – The Hidden Access Hole
🔐 Control Focus: Identify and Audit Orphaned MFA Devices
🧠 Objective: Prevent unauthorized access through inactive, forgotten, or misassigned MFA tokens and devices.
📌 Framework Mapping:
- ISO/IEC 27001 – A.5.17 (Authentication)
- NIST SP 800-53 – IA-2 (Identification and Authentication)
- CloudCSF Domain – Identity & Access Assurance
🚨 Why This Control Matters:
Organizations implement MFA, but often fail to revoke, rotate, or monitor devices after employee exits, role changes, or mobile phone losses. These orphaned MFA tokens are the Achilles’ heel of Zero Trust, providing potential backdoors for attackers, insiders, or rogue automation scripts.
🧭 Audit Actions Checklist:
✅ Inventory all MFA-registered devices per user
✅ Cross-check with HR offboarding and IT access logs
✅ Disable MFA for terminated users or devices with no recent auth attempts
✅ Flag users with multiple unverified MFA devices
✅ Automate alerts for MFA tokens unused for 30+ days
📊 Risk Impact:
An orphaned MFA token tied to a privileged account or forgotten API key can bypass layered security when combined with stale credentials or shared secrets. This negates the entire Zero Trust posture and introduces silent breach potential.
📥 Free Download:
👉 Grab the “Orphaned MFA Audit Tracker” (Excel + PDF) to start assessing your environment today.
🧠 Bonus Tip:
MFA hygiene is not just about enforcing MFA — it’s about ensuring active lifecycle management. Integrate decommission triggers, HR feeds, and behavioral analytics to automate MFA cleanup.
🎯 Call to Action:
Want help designing a bulletproof IAM program?
📩 Drop “MFA-34” in the contact with your details or join our WhatsApp Group »