
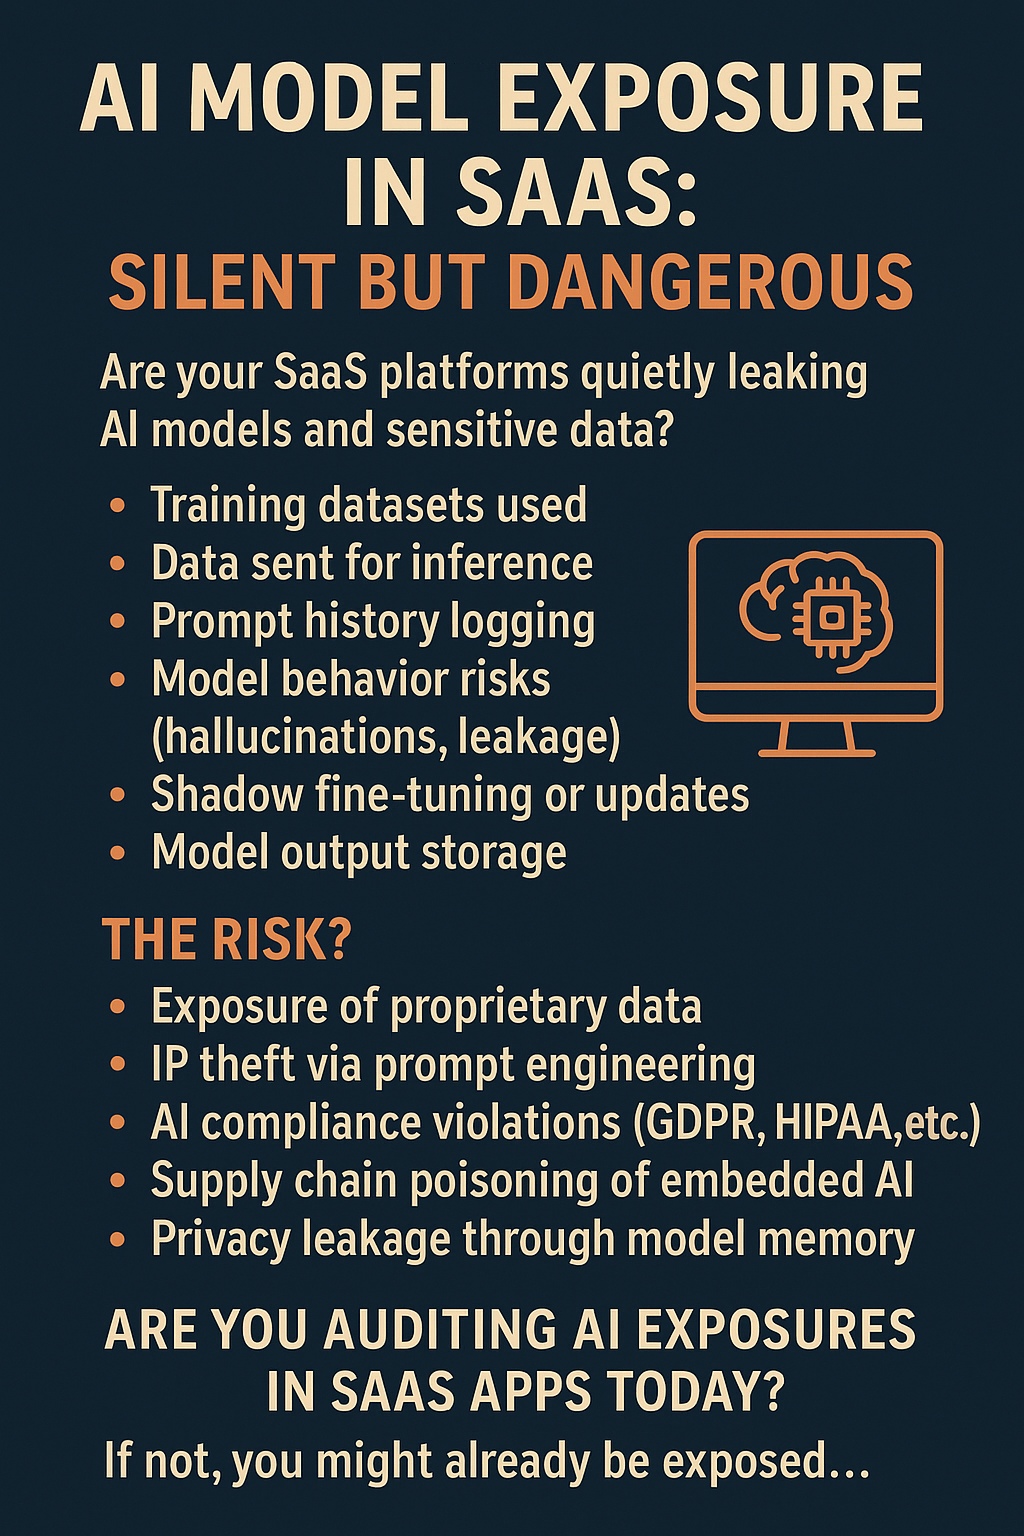
🔥 Day 39: Why You Must Audit AI Model Access Today — Before It’s Too Late!
🚨 Hidden Threat:
Every time your AI model is exposed via a public endpoint, shadow developer, or untracked CI/CD call, you’re widening the attack surface for AI Prompt Injection, Model Theft, or Data Leakage.
🔍 Case in Point:
A global fintech firm had its sentiment analysis model hijacked via a forgotten API. Attackers fed malicious prompts and extracted training data — bypassing security controls completely.
💡 Quick Questions to Ask Today:
- Who can access your AI models (internally or externally)?
- Are you logging prompt injections, drift behaviors, or adversarial input attempts?
- Do you maintain an AI Exposure Register and update it monthly?
- Do you run Red Team simulations on your GenAI/LLM assets?
📥 Free Templates You Can Use Now:
✅ [AI Model Exposure Tracker – Excel + PDF Templates]
✅ [Prompt Injection Risk Control Checklist]
✅ [AI Risk Register – ISO 42001 Aligned]
🔐 Final Thought:
AI isn’t secure by default. Just like cloud workloads, AI models must be audited, versioned, and monitored as part of your Digital Trust DNA.
💬 What’s your AI security readiness score?
👇 Share your top AI security concern in the comments.
🔁 Repost to help your peers avoid AI chaos.
#AIModelSecurity #AIGovernance #CybersecurityLeadership #CloudSecurity #PromptInjection #AIExposure #ISO42001 #ModelRisk #CISO2AI #AuditSecIntel