
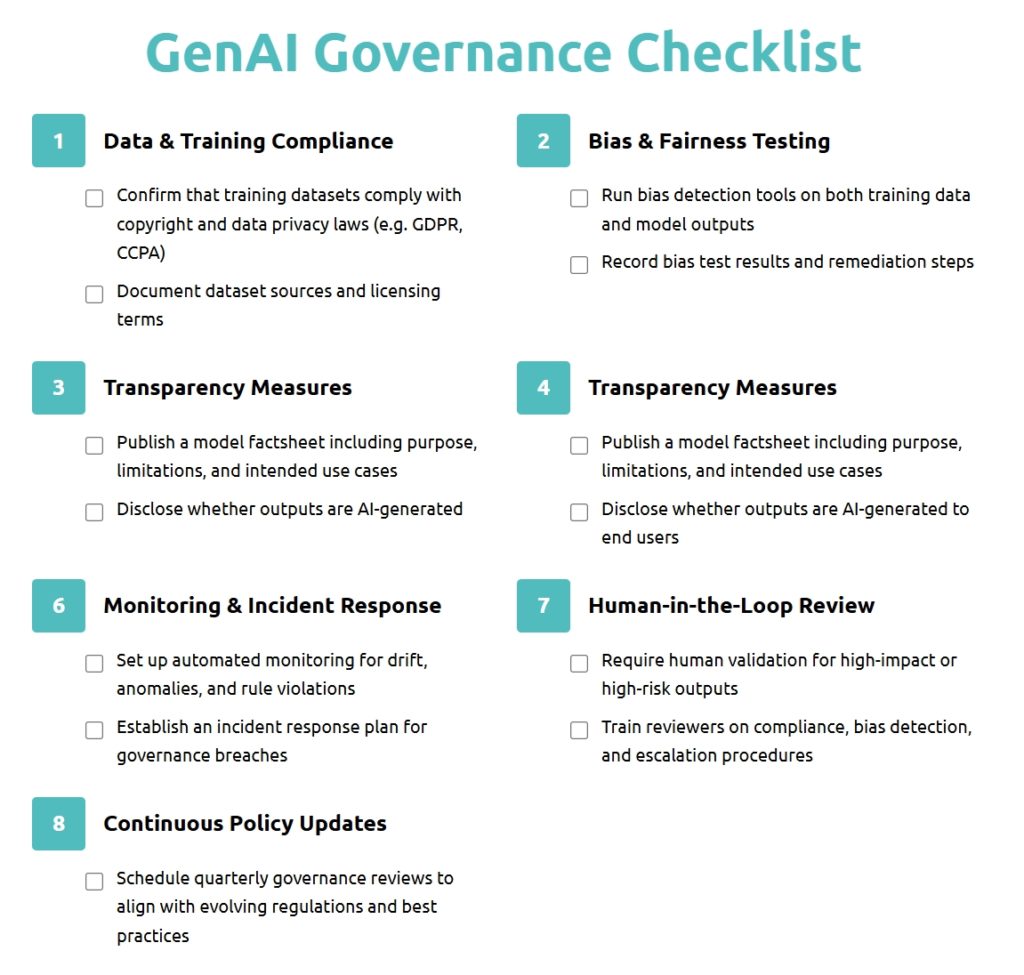
“Your AI Might Be Compliant — But Can You Prove It?”
🧠 Key Point
In cybersecurity, intent doesn’t matter.
Evidence does.
AI is no different.
🚨 CloudCSF Insights
Many organizations confidently say:
- “We use AI responsibly.”
- “We have AI policies.”
- “We follow best practices.”
But when regulators, auditors, or the board ask:
❓ Show me where this AI is used
❓ Show me who approved the data
❓ Show me how risk was assessed
❓ Show me how decisions are monitored
Silence follows.
Not because controls don’t exist —
but because evidence was never designed.
This is the AI Evidence Gap.
AI programs are often:
- Built fast
- Adopted widely
- Governed verbally
- Documented late
And that’s a problem.
Because AI risk isn’t judged by what you believe —
it’s judged by what you can demonstrate.
🧭 The CloudCSF Reframe
AI governance must be evidence-first, not policy-first.
CISOs must ensure:
- 📂 AI inventories are current
- 🧾 Risk assessments are recorded
- 🔁 Changes are reviewable
- 📊 Decisions are traceable
- 🧑⚖️ Accountability is provable
If AI governance can’t produce evidence on demand,
it doesn’t exist in the eyes of auditors.
✅ Action for Today (CISO Move)
Ask this simple but revealing question:
“If we were audited tomorrow, what AI evidence could we produce in 24 hours?”
If the answer is fragmented,
your AI risk posture is fragile — regardless of controls.
🧩 Closing Thought
We learned this lesson with cloud and privacy:
- Controls without evidence fail audits
- Good intent doesn’t survive scrutiny
AI will be no different —
except scrutiny will arrive faster and harsher.
CloudCSF exists to help CISOs move from
AI promises → AI proof → AI trust.
🔖 Hashtags
#CloudCSF #AIGovernance #AICompliance #AISecurity #CISO2_0 #CyberGRC #DigitalTrust #ISO42001 #NISTAIRMF #AITrust #ResponsibleAI #SecurityLeadership