
🔥 CloudCSF – January 2026
“Your AI Didn’t Get Hacked — Your Data Did. Welcome to the RAG Risk Era.”
🧠 CISOs spent years protecting systems.
2026 will punish those who don’t protect AI knowledge pipelines.
🚨 AI Security – Are you ready ?
Everyone is talking about AI models.
Almost no one is auditing what those models retrieve.
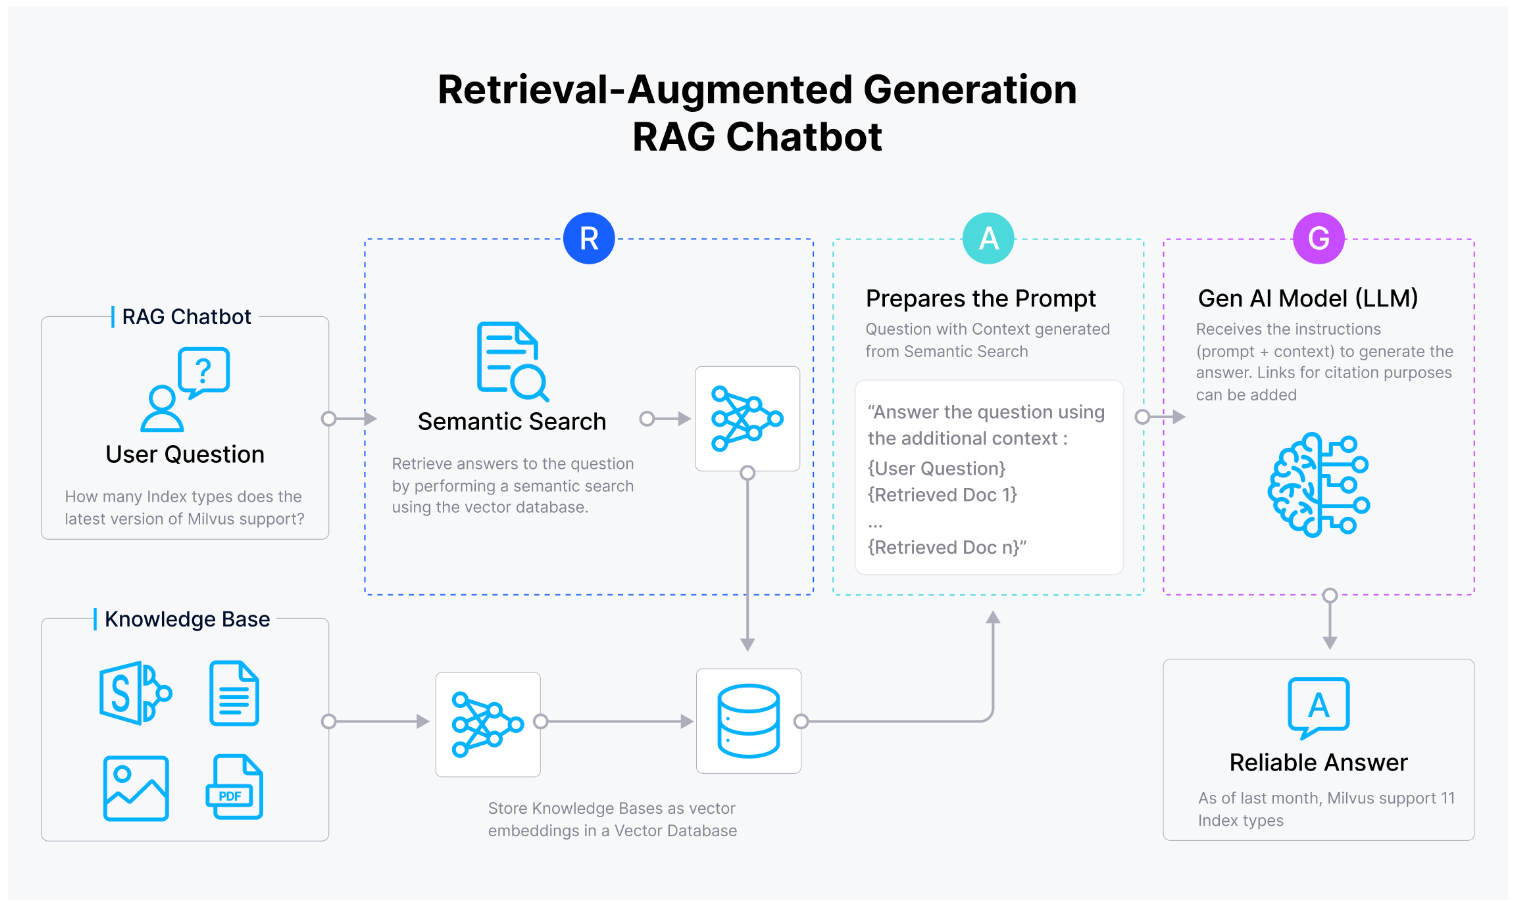
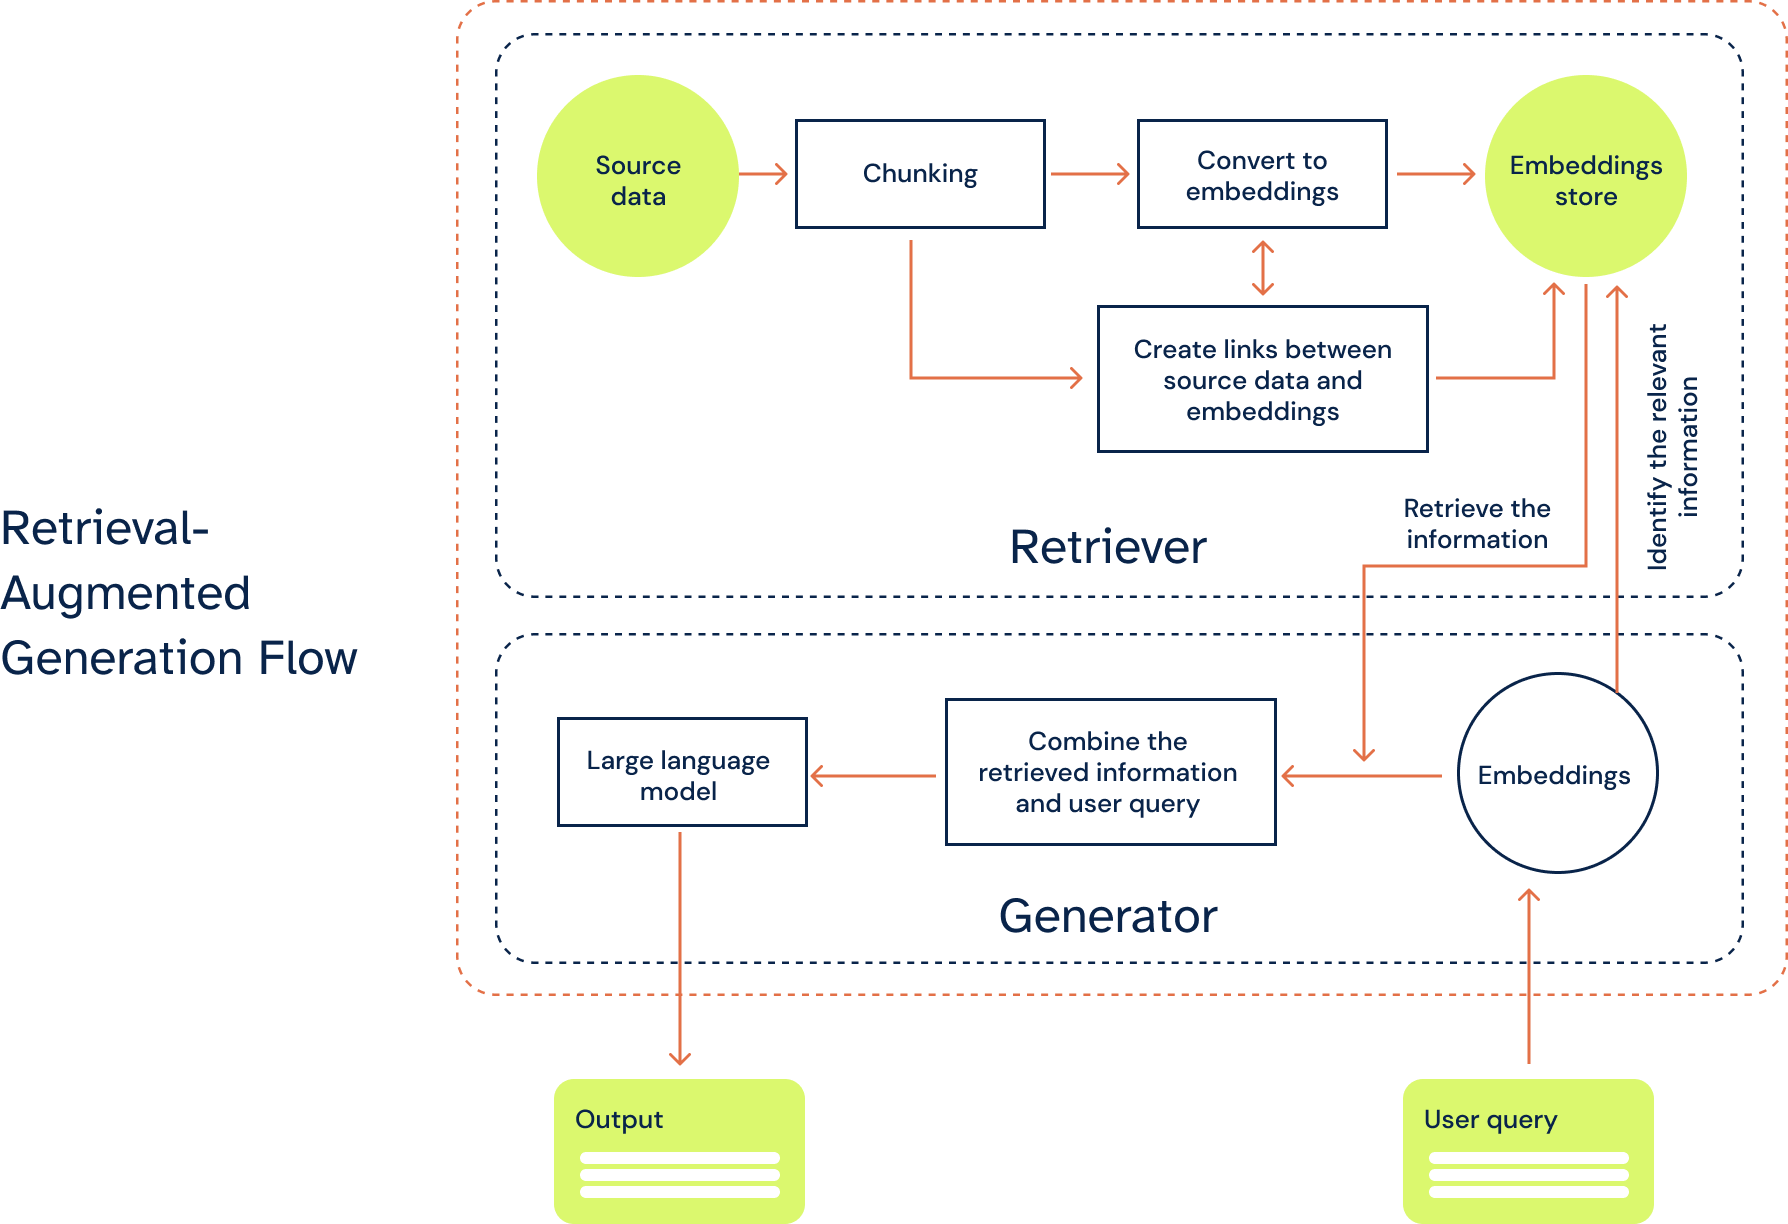
In 2026, most enterprise AI is no longer just LLMs.
It’s RAG-powered AI — connected to:
- Vector databases
- Internal documents
- Tickets, emails, policies
- Customer data
- Knowledge bases
Here’s the dangerous truth 👇
❌ You can secure the model
❌ You can restrict the user
❌ You can monitor prompts
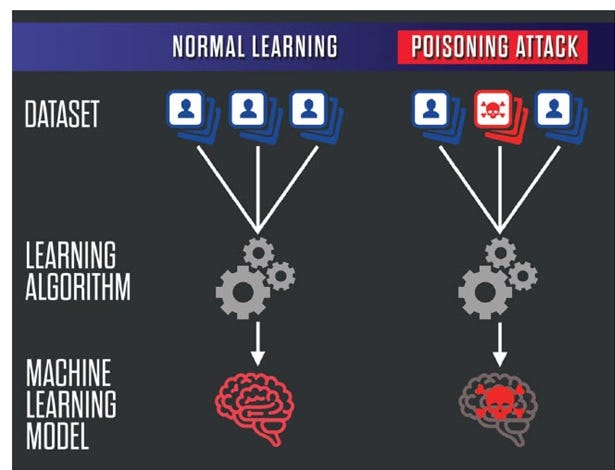
…but if your retrieval layer is poisoned, stale, or over-permissive,
your AI will confidently deliver wrong, leaked, or manipulated answers.
⚠️ This is not a future risk.
This is a 2026 breach pattern.
If you’re not asking:
❓ Which data sources feed each AI system?
❓ Who approves what gets embedded into vectors?
❓ How often is RAG data reviewed, refreshed, or revoked?
❓ Can attackers influence AI answers without touching the model?
Then your AI is already lying with authority.
✅ Action for 2026 (High-Value & Practical)
📥 Download: “AI RAG Data Exposure & Poisoning Risk Tracker” (Excel + PDF)
A CloudCSF™ micro-tool built for real enterprise AI governance
What this mini-product helps you do:
✔ Inventory RAG data sources (files, DBs, APIs)
✔ Identify sensitive & regulated data inside vector stores
✔ Detect stale, unowned, or unreviewed embeddings
✔ Score data poisoning & leakage risk (RAG-specific)
✔ Map findings to ISO 42001 & NIST AI RMF
📊 Built-in value:
- Auto RAG risk scoring
- High-risk knowledge source heatmap
- Review frequency tracker
- Board-ready executive summary PDF
👉 In 2026, AI trust = Data trust.
If you don’t govern retrieval, you don’t govern AI.
🔗 Download Now
📥 AI RAG Data Exposure & Poisoning Risk Tracker (Excel + PDF)
👉 [Contact to Get CloudCSF Download / Razorpay / Stripe Link]
💡 Why This Post Is Different
Most AI posts talk about:
- Prompts
- Models
- Policies
This one talks about truth integrity.
👉 The fastest way to destroy AI trust
is not hacking the model —
it’s quietly changing what the AI believes.
That’s CISO 2.0 thinking.
That’s CloudCSF 2026 readiness.
Hashtags
#CloudCSF #RAGSecurity #AIDataRisk #AIGovernance
#ISO42001 #NISTAIRMF #CISO2_0 #AISecurity
#DigitalTrust #AITruth #CyberGRC #AIExposureRisk