
Here is your CloudCSF – Day 24 High-Value Blog Post
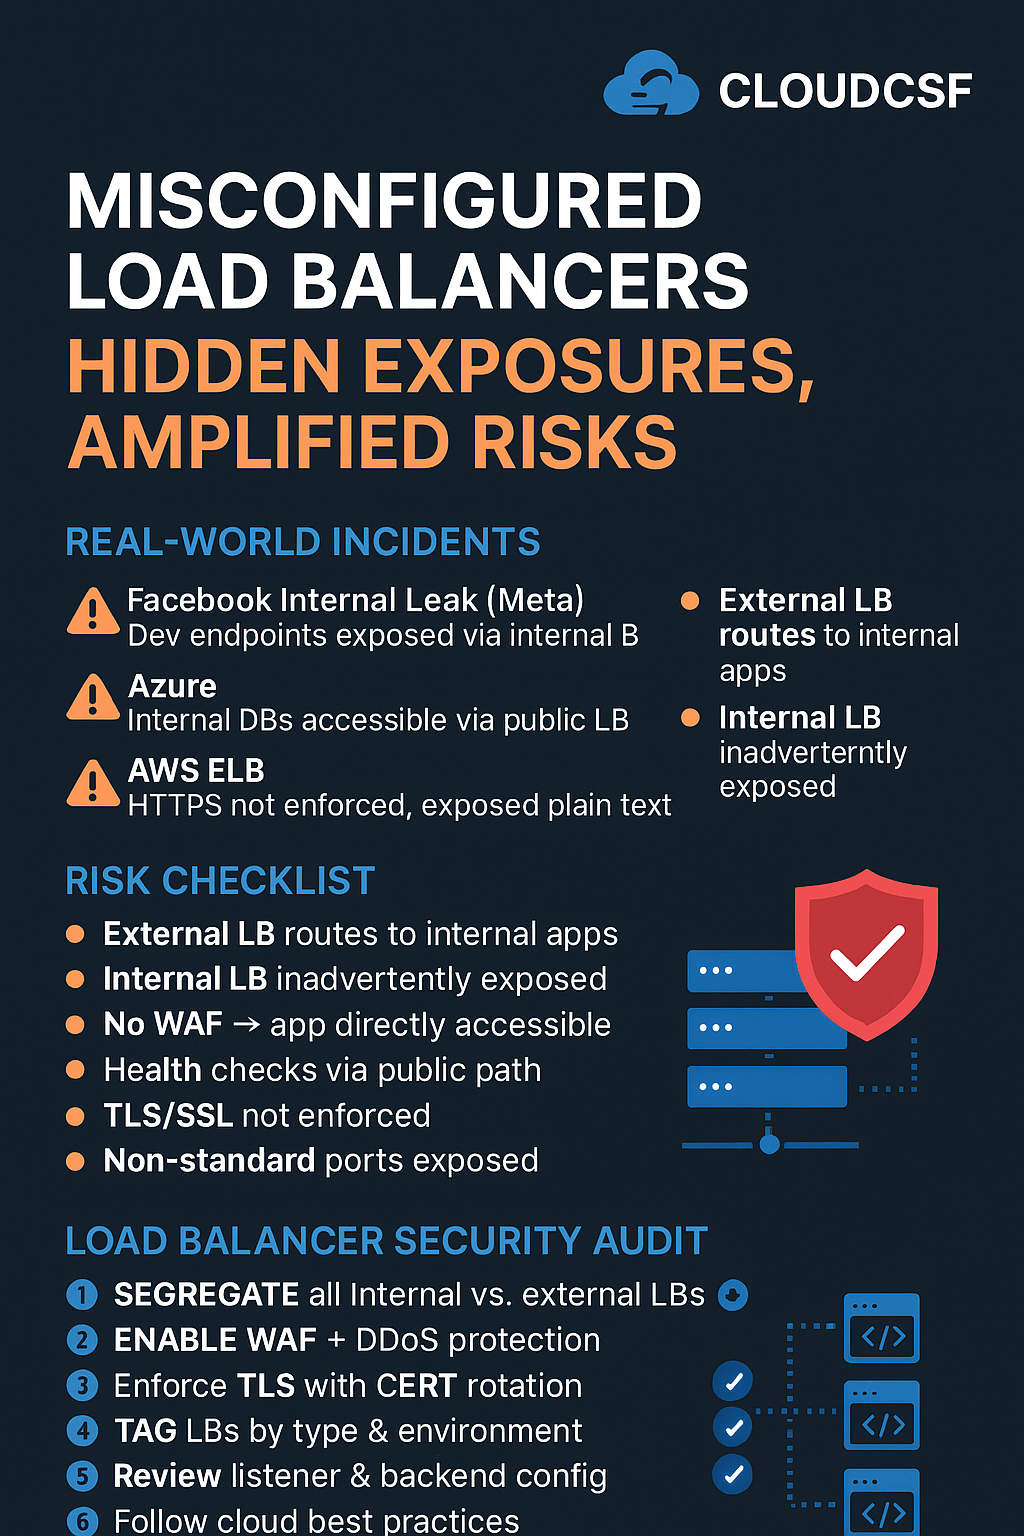
🔐 Control #23: Misconfigured Load Balancers — Hidden Exposures, Amplified Risks
🌀 CloudCSF – Day 24
Control #23: Misconfigured Load Balancers — The Gateway to Internal Chaos
“Your load balancer is either your security perimeter’s best friend… or its worst enemy.”
🚨 Why This Control Matters
Misconfigured cloud load balancers (LBs) often:
- Route traffic to staging or internal services
- Skip web application firewalls (WAFs) or auth checks
- Expose internal ports (e.g., gRPC, SSH, databases) via HTTPS listener
- Misuse TLS/SSL certificates — or leave them expired
⚠️ Real-World Mistakes That Cost Millions
| Case | Impact |
|---|---|
| Facebook Internal LB Leak (Meta) | Exposed dev endpoints accessible to public internet |
| Misrouted LB in Azure | Internal DBs served through public HTTP |
| No SSL LB (AWS ELB) | Financial app exposed unencrypted data in transit |
📌 Risk Checklist
- Public LB routing to internal services (via private IP)
- Internal LB mistakenly exposed via DNS or IP
- WAF not integrated in front of Load Balancer
- Backend services allow unauthenticated access
- Health checks routed via public path
- No TLS enforcement or HTTP fallback allowed
- Excessive ports (8080, 8443, 3000) open in listener rules
🛠️ CloudCSF Load Balancer Misconfiguration Framework
- Segregate Load Balancer Types
- Public → Internet-facing apps only
- Internal → Private apps (monitoring, APIs, admin panels)
- Integrate WAF + DDoS Protections
- AWS WAF / Azure WAF / Cloud Armor
- Enforce OWASP rulesets and rate limiting
- TLS Everywhere + Cert Management
- Use ACM (AWS) / Key Vault (Azure) / Cert Manager (GCP)
- Rotate certs and disable HTTP fallback
- Tag All LBs
- Tag as
Public,Internal,Production,Dev,Exempt, etc. - Helps avoid routing mix-ups during IaC updates
- Tag as
- Perform LB Security Audit
- Are all listeners secure?
- Any unused rules?
- Backend auth enforced?
- Cloud-Native Best Practices
- Use HTTPS health checks
- Restrict IP range for admin panels
- Don’t route dynamic dev URLs from static prod LBs
🔄 Maturity Levels
| Level | Description |
|---|---|
| 🔴 L0 | No LB tagging or segregation; public/internal mixed |
| 🟠 L1 | Partial segregation; weak cert handling |
| 🟡 L2 | TLS enforced; no WAF |
| 🟢 L3 | Tagged, segregated, WAF-protected LBs |
| 🔵 L4 | Fully auditable, auto-remediated via IaC policies |
📊 Tools for Load Balancer Posture Management
- AWS ELB Analyzer, Azure Front Door Metrics
- GCP Load Balancer Insights
- Wiz, Orca, Prisma — for misrouting detection
- Terraform Sentinel/OPA — for policy enforcement
📝 Free Download:
Cloud Load Balancer Security Audit Checklist (XLSX + PDF)
🔍 Audit every LB in your org across AWS, Azure, and GCP.
📆 Tomorrow’s Post
Day 25 – Control #24: Credential Hardcoding in Scripts and Repos — The Developer Trap
Load Balancer Security, Cloud Load Balancer Audit, Misconfigured Load Balancer, Public vs Internal LB, TLS in Load Balancers, WAF Integration Checklist, Cloud Network Security, AWS ELB Security, Azure Front Door Audit, GCP Load Balancer Security