
🛡️ CloudCSF – Day 26
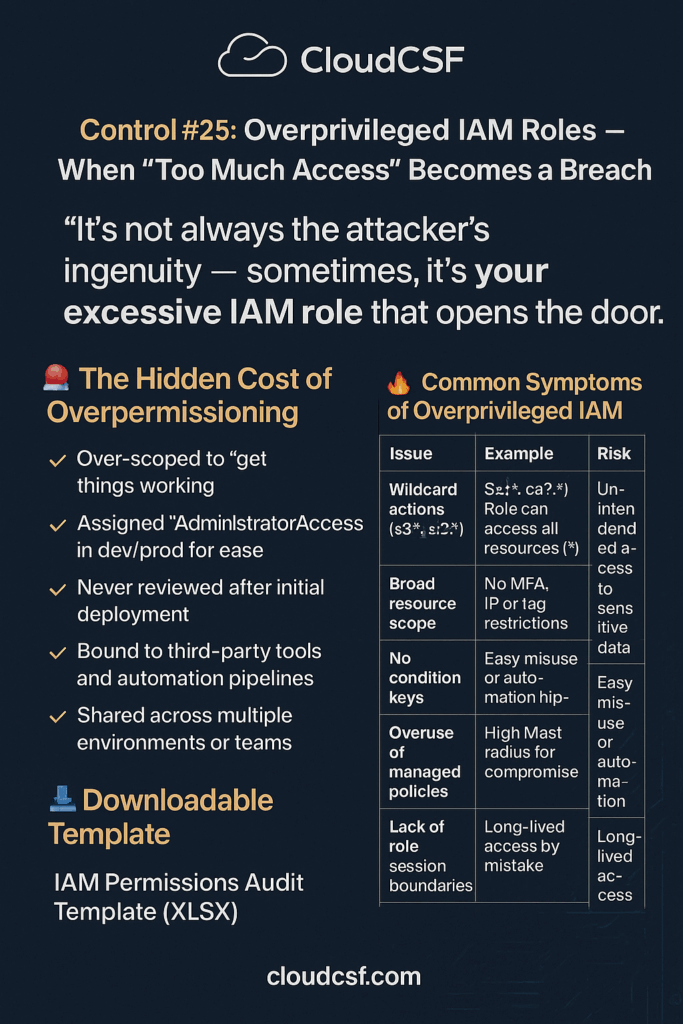
Control #25: Overprivileged IAM Roles — When “Too Much Access” Becomes a Breach
“It’s not always the attacker’s ingenuity — sometimes, it’s your excessive IAM role that opens the door.”
🚨 The Hidden Cost of Overpermissioning
IAM Roles are often:
- Over-scoped to “get things working”
- Assigned
AdministratorAccessin dev/prod for ease - Never reviewed after initial deployment
- Bound to third-party tools and automation pipelines
- Shared across multiple environments or teams
These IAM roles become “keys to the kingdom”, abused in:
- Lateral movement
- Data exfiltration
- Privilege escalation
- Persistence in cloud environments
🔥 Common Symptoms of Overprivileged IAM
| Issue | Example | Risk |
|---|---|---|
Wildcard actions (s3:*, ec2:*) | Dev role can access any S3 bucket | Unintended access to sensitive data |
| Broad resource scope | Role can access all resources (*) | Full infra takeover possible |
| No condition keys | No MFA, IP or tag restrictions | Easy misuse or automation hijack |
| Overuse of managed policies | Attachments like PowerUserAccess | High blast radius for compromise |
| Lack of role session boundaries | No MaxSessionDuration enforced | Long-lived access by mistake |
🔍 Audit Tips for CloudCSF Implementation
✅ Identify all roles with:
AdministratorAccess,PowerUserAccess,FullAccess- Wildcard permissions (
*:*) - No session restrictions
- No recent usage (stale roles)
✅ Run IAM Access Analyzer (AWS) or Policy Insights (Azure)
✅ Audit assume-role trust policies
- Who can assume this role?
- Are third-party vendors involved?
🛠️ Least Privilege Design Practices
🔹 Use resource-level restrictions
🔹 Avoid wildcard actions and resources
🔹 Apply MFA requirement, IP allow-lists, tags
🔹 Create custom policies for each workload
🔹 Enforce role session duration limits (max 1h)
🔹 Rotate access keys every 90 days
🧠 CloudCSF Maturity Model – IAM Permissions
| Level | Description |
|---|---|
| 🔴 L0 | Wildcards, admin roles everywhere |
| 🟠 L1 | Some MFA, but no granular scopes |
| 🟡 L2 | Role segmentation begins |
| 🟢 L3 | Role assumption & permission boundaries |
| 🔵 L4 | Automated least-privilege enforcement & drift detection |
📥 Downloadable Template
🎯 IAM Permissions Audit Template (XLSX)
Track overprivileged roles, access boundaries, and stale role remediation.
🗓️ Tomorrow’s Preview
Day 27 – Control #26: Insecure CI/CD Pipeline Permissions & Secrets