
Here is your CloudCSF – Day 27 High-Value Post
🧠 Control #26: CI/CD Pipelines with Excessive Permissions & Secrets Exposure
🚨 CloudCSF – Day 27
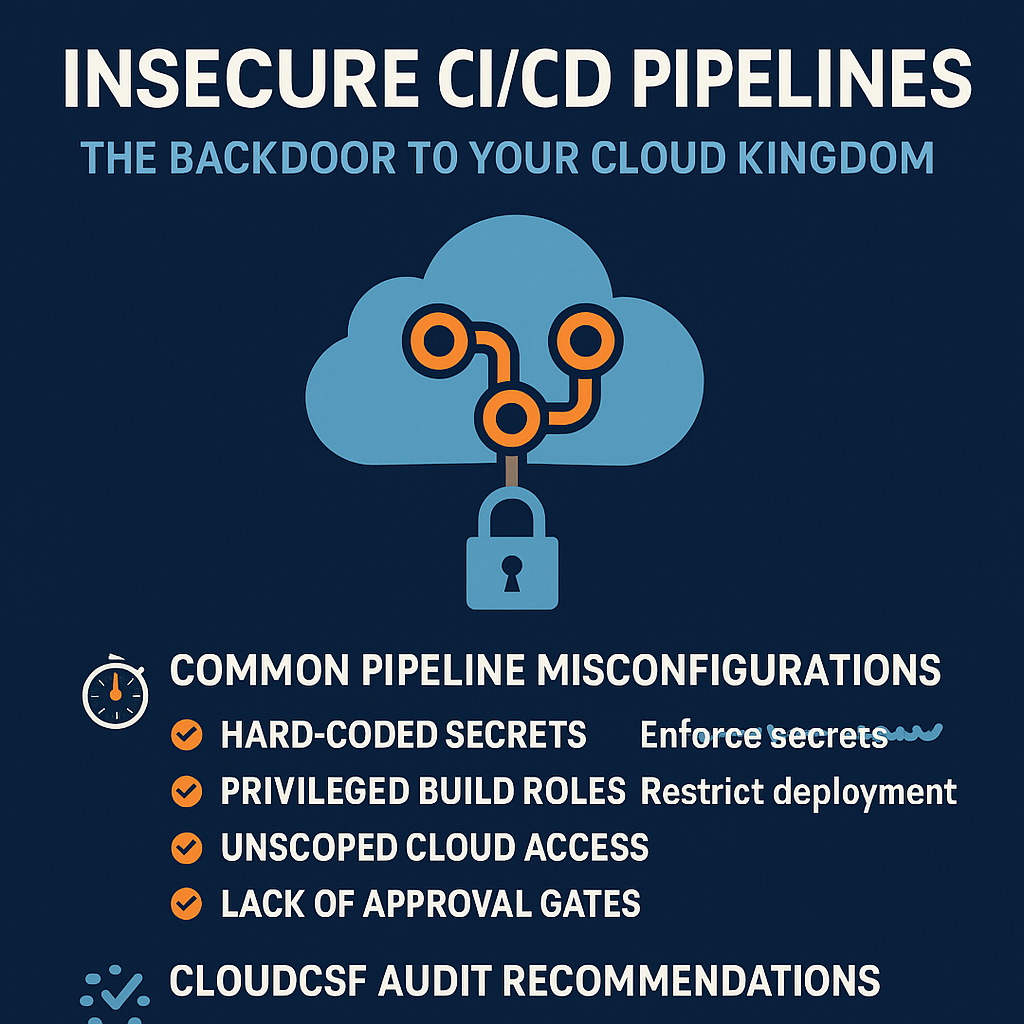
Control #26: Insecure CI/CD Pipelines – The Backdoor to Your Cloud Kingdom
“The CI/CD pipeline that deploys your cloud… can also destroy it.”
🔓 Why CI/CD Is a Prime Attack Target
Modern DevOps pipelines (GitHub Actions, GitLab CI, Jenkins, CircleCI, etc.) often:
- Have excessive IAM or cloud access (
admin,fullAccess) - Store secrets in plaintext env vars or config files
- Trigger workflows from untrusted pull requests
- Use outdated runners or self-hosted agents without patching
- Push to cloud infra without verification or security gating
😱 Common Pipeline Misconfigurations
| Misconfig | Impact |
|---|---|
AWS_ACCESS_KEY hardcoded in workflows | Full S3/EC2 compromise |
Secrets in .env, config.json, or YAML | Easy to leak in PRs |
| Privileged deploy role used in every job | Total blast radius |
| No source IP allowlist | Attackers can exploit public webhooks |
| No workflow approval | Any user push can auto-deploy to prod |
✅ CloudCSF Audit Recommendations
🔍 Audit Checklist
- Review IAM roles assigned to runners
- Ensure secrets are rotated, not hardcoded
- Enforce workflow approval gates for production
- Limit pipeline access to specific environments
- Require code review before deployment steps
🛡️ Tools to Automate Audit:
Checkov,Trivy,gitleaks,kics, GitHubsecret scanningAWS CodeGuru,Azure DevOps Analyzer,OWASP SCM Security Guide
🧠 CloudCSF Maturity Model – CI/CD Security
| Level | Description |
|---|---|
| 🔴 L0 | No review, admin roles, plaintext secrets |
| 🟠 L1 | Manual approval, but secrets still exposed |
| 🟡 L2 | Scoped roles, automated scans |
| 🟢 L3 | Signed commits, secure runners |
| 🔵 L4 | Zero-trust pipeline, full audit logging, access gating |
📥 Download the Audit Template
📄 CI/CD Pipeline Risk Audit Template (PDF) – Use contact to get this
👀 Use this to check permissions, secrets, access scopes, and deploy risks.
🗓️ Coming Tomorrow
Day 28 – Control #27: Shadow API Exposure – Your Cloud’s Hidden Entry Points