
Here is your CloudCSF – Day 30 High-Value Blog Post
🧠 Control #29: Cloud Resource Tagging Enforcement – Know Who Owns What
🌐 CloudCSF – Day 30
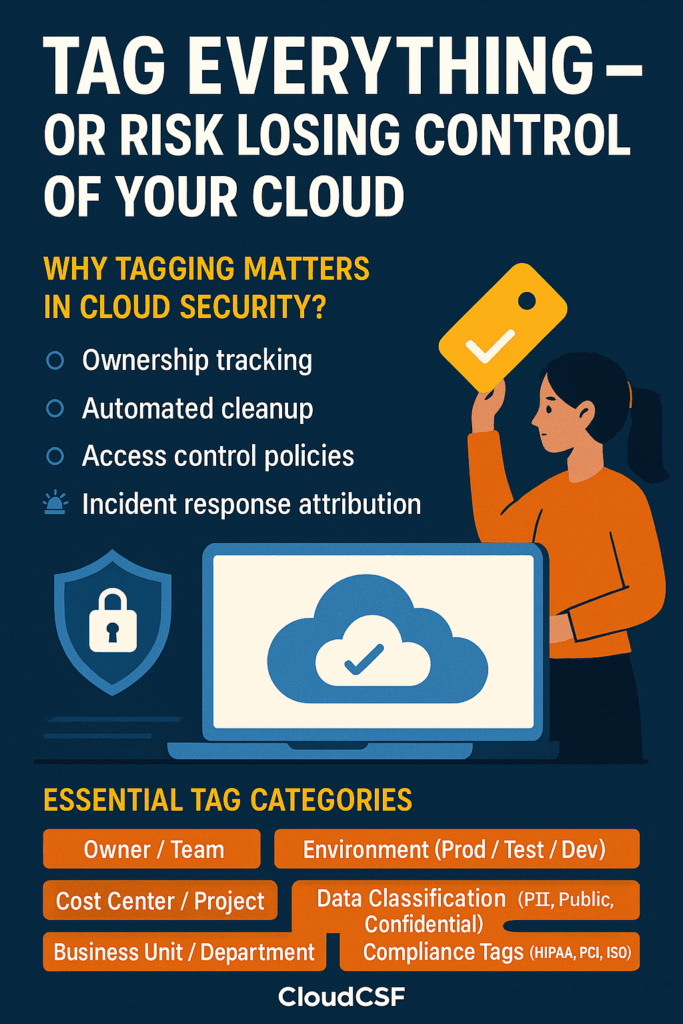
🔖 Control #29: Tag Everything – Or Risk Losing Control of Your Cloud
“If it’s not tagged, it’s not trusted.”
🔍 Why Tagging Matters in Cloud Security
Tagging isn’t just for billing. It enables:
- Ownership tracking 🧑💼
- Automated cleanup 🧹
- Access control policies 🔐
- Incident response attribution 🚨
⚠️ What Happens Without Tagging?
| Issue | Consequence |
|---|---|
| No Owner Tag | No one accountable for the resource |
| No Environment Tag | Can’t isolate production from test |
| No Purpose Tag | Hard to identify critical workloads |
| No Data Sensitivity Tag | Poor data classification for compliance |
🧩 Essential Tag Categories
- Owner / Team
- Environment (Prod/Test/Dev)
- Cost Center / Project
- Data Classification (PII, Public, Confidential)
- Business Unit / Department
- Compliance Tags (HIPAA, PCI, ISO)
✅ CloudCSF Enforcement Practices
🔧 Automated Enforcement:
- Use tools like AWS Config Rules, Azure Policy, or GCP Organization Policies
- Block resource creation if key tags are missing
📦 Tools to Enforce/Track Tags:
- Cloud Custodian
- Steampipe
- Yor (Automated Tag Insertion)
- Datadog Tag Explorer
📈 CloudCSF Maturity – Tagging Compliance
| Level | Tagging Hygiene |
|---|---|
| 🔴 L0 | No tagging enforced |
| 🟠 L1 | Tags applied manually |
| 🟡 L2 | Partial automation |
| 🟢 L3 | Tags required at creation, audit monthly |
| 🔵 L4 | Fully automated with tagging scorecard and dashboards |
📥 Download
✅ Public IP Exposure Tracker (XLSX)
📄 Tagging Compliance Tracker – Coming Soon!
🎯 Final CloudCSF Message:
Security Maturity = One Control at a Time
Tag it, Track it, Trust it.