
✅ CloudCSF – Day 36: “Undiscovered Third-Party API Keys – The Blind Spot in Cloud Breaches”
🎯 Objective:
Highlight the risks of untracked or unused third-party API keys integrated into cloud platforms and help security teams build a centralized discovery and revocation strategy.
🚨 The Growing Threat:
APIs are the glue of modern cloud architecture—but with flexibility comes exposure. Many organizations:
- Integrate SaaS tools using API keys without expiry.
- Leave API tokens in code, GitHub repos, or CI/CD tools.
- Never audit who issued the keys, for what purpose, or when last used.
Result?
Compromised keys = Full access to your cloud or data APIs.
And attackers know it.
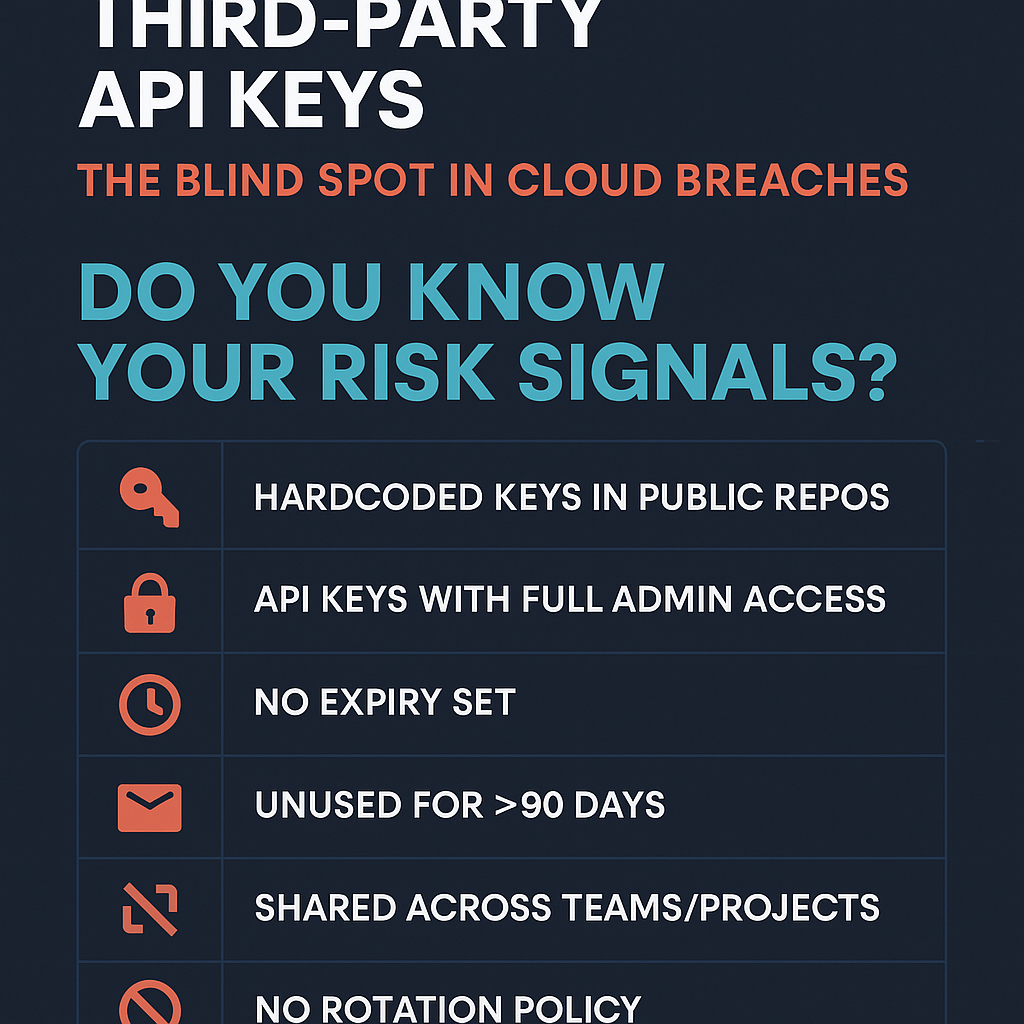
🔍 API Key Risk Signals:
| Signal | Description | Risk |
|---|---|---|
| 🗝️ Hardcoded keys in public repos | Exposed in GitHub, GitLab, Bitbucket | 🔴 High |
| 🔓 API keys with full admin access | No least privilege applied | 🔴 High |
| 🕒 No expiry set | Infinite lifetime = infinite risk | 🟠 Medium |
| 📭 Unused for >90 days | Indicates forgotten/abandoned | 🟡 Medium |
| 🔁 Shared across teams/projects | No owner accountability | 🔴 High |
| ❌ No rotation policy | Old tokens still active | 🟠 Medium |
📋 Your Next Steps:
- Discover:
Use scanning tools to find exposed API keys in:- Git repos
- Slack, Teams, email
- Environment variables
- Tag & Inventory:
Build a central inventory of API keys with metadata:- Created by, for, scope, expiry, last used
- Enforce Least Privilege:
- Restrict access per API service.
- Avoid “god-mode” tokens for automation.
- Automate Revocation:
- Revoke keys older than 90 days or unused.
- Continuous Monitoring:
Integrate with CI/CD to detect exposed keys in PRs.
📉 Real Breach Snapshot:
In a 2024 breach, attackers leveraged a Jira API token found in a developer’s GitHub issue comment. The token had admin access to the company’s cloud infra—no alerts, no expiry, full compromise.
📥 Download:
🔐 [API Key Inventory & Risk Audit Template – Excel + PDF]
🛡️ Bonus:
✅ Auto-tag API tokens in AWS, Azure, and GCP
✅ Monthly audit reminder template
✅ Link API key rotation with IAM offboarding workflows
📣 Call to Action:
Share this with your DevOps, CloudSec & IAM teams.
Turn unknown API keys into zero-trust managed assets.
Disclaimer: This post provides general information and is not tailored to any specific individual or entity. It includes only publicly available information for general awareness purposes. Do not warrant that this post is free from errors or omissions. Views are personal