
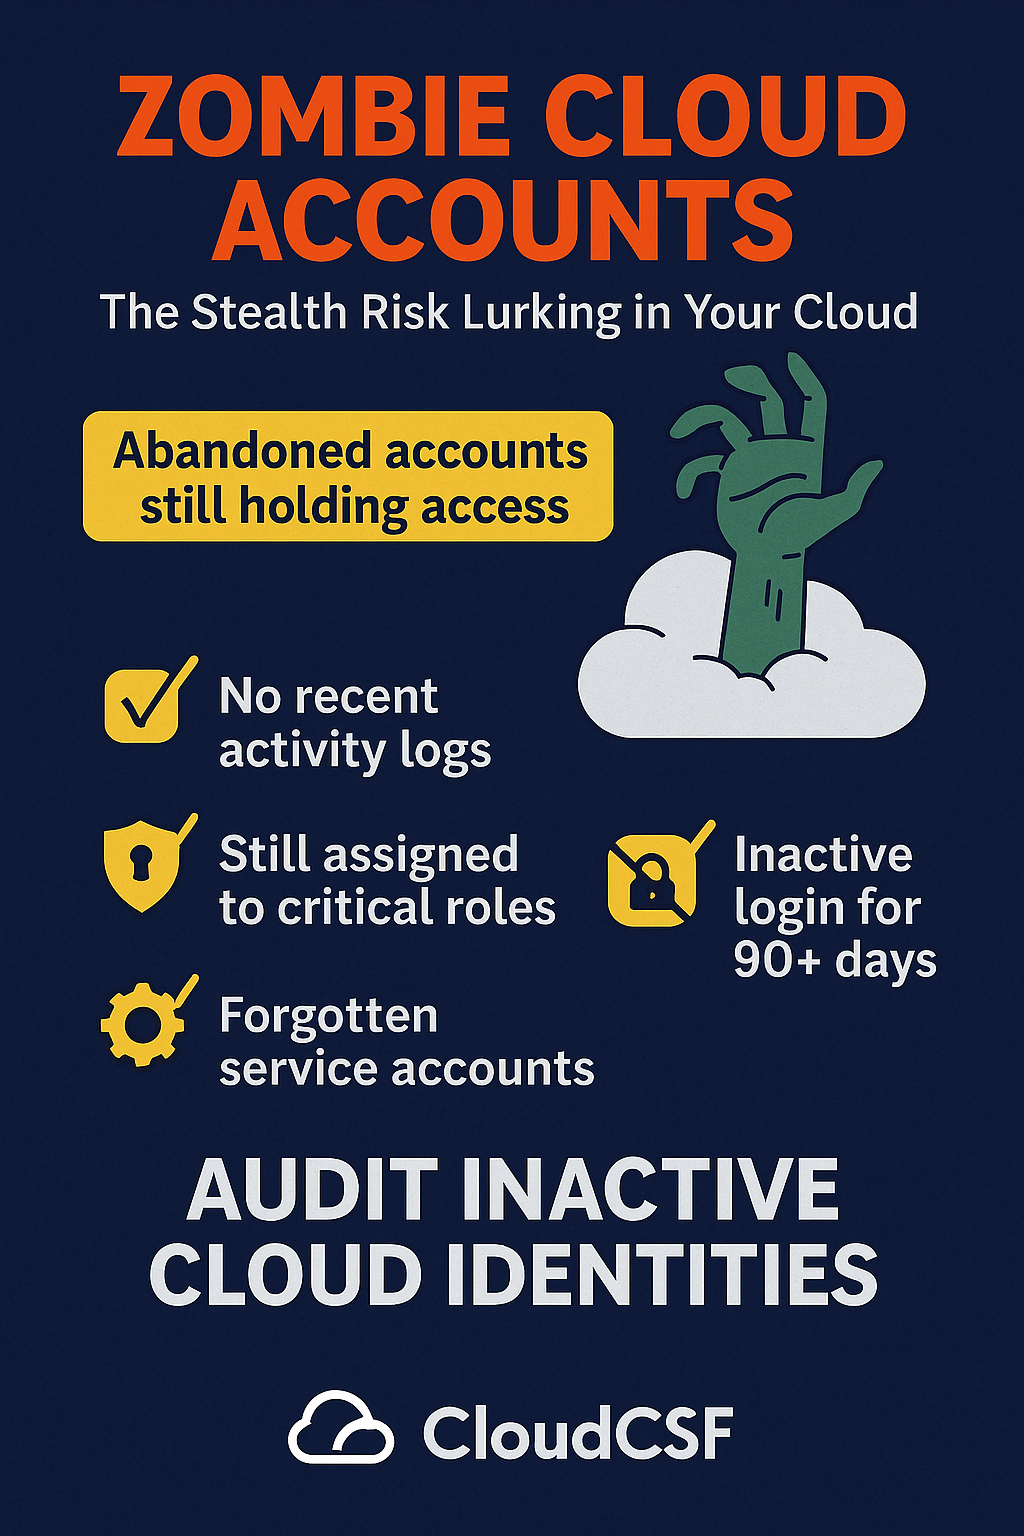
✅ CloudCSF – Day 31: The Phantom Menace of Zombie Cloud Accounts
🔐 Post Title:
Zombie Cloud Accounts: The Stealth Risk Lurking in Your Cloud
🧠 What It’s About:
Zombie accounts are deactivated or abandoned cloud identities that still hold access rights. These often exist long after the user, service, or workload is gone — but they still have login capabilities or API access tokens active!
🚨 The Hidden Dangers:
- ✅ They bypass most active IAM checks.
- ✅ Rarely appear in standard role reviews.
- ✅ Attackers can exploit them quietly.
- ✅ Major contributor to lateral movement and privilege escalation in breach scenarios.
🔎 Key Indicators of Zombie Accounts:
- No recent activity logs
- Still assigned to critical roles
- Inactive SSO or password login for 90+ days
- Forgotten service accounts with active credentials
🛡️ Audit Actions You Can Take Today:
- 🔄 Review all inactive cloud identities older than 60–90 days.
- 📤 Enable auto-expiration policies.
- 🧹 Tag & archive obsolete workloads and their IAM roles.
- 💣 Use a “last-seen” audit tracker (We’ll provide one tomorrow!)
📥 Download Coming Tomorrow:
Zombie Account Audit Tracker (Excel + PDF)
🔗 #CloudSecurity #IAMAudit #ZombieAccounts #CloudRisk #CybersecurityPost #CloudCSF #Misconfigurations #SecurityAudits
Disclaimer: This post provides general information and is not tailored to any specific individual or entity. It includes only publicly available information for general awareness purposes. Do not warrant that this post is free from errors or omissions. Views are personal