
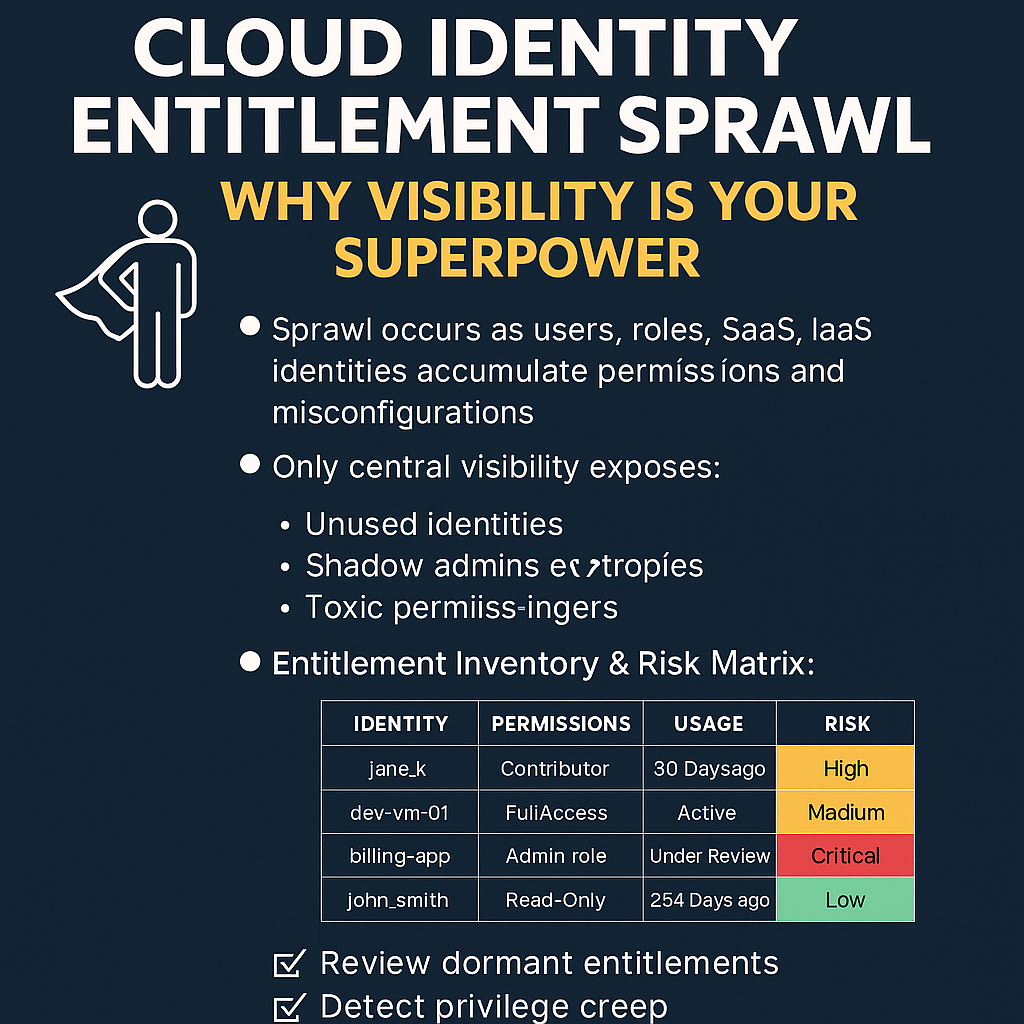
Topic: “Cloud Identity Entitlement Sprawl – Why Visibility is Your Superpower”
🧠 Quick Insight:
In modern multi-cloud environments, every identity—whether user, service, or workload—can accumulate entitlements rapidly. Over time, this creates a cloud identity sprawl where users, roles, and policies overlap dangerously.
🚨 When left unchecked:
- Users hold permissions they don’t need.
- Shadow admins emerge without notice.
- Toxic permission combinations arise.
- SaaS and multi-cloud identities become invisible in silos.
🔎 Control Insight:
✅ CSPM and CIEM tools alone can’t fix what you can’t see.
✅ You must track:
- Who has access
- What they can do
- Where those permissions are active
- When those were last used
📊 Action Template (Download link will follow):
“Entitlement Inventory & Risk Matrix”
- Identity → Permissions → Usage → Criticality
- Risk Scoring with color-coded indicators
- Filter by cloud, region, app, group, and role
💡 CloudCSF Tip:
🔄 Review entitlements every 30 days.
📉 Track privilege drift and revoke unused access.
🧩 Map IAM policies to workloads and APIs.
🎯 Why This Matters:
Identity is the new perimeter.
But unmonitored identity sprawl is a threat actor’s dream.
📢 CTA:
🚀 Download the Entitlement Risk Matrix Tracker (Excel + PDF)
🛡️ Practice Zero Standing Privilege (ZSP)
🧠 Adopt Cloud Identity Governance by Design
🔗 #CloudCSF #IdentitySecurity #CIEM #IAMAudit #EntitlementReview #PrivilegeCreep #ZombieAccounts #CloudGovernance #CyberRisk #CSPM #ZeroTrust
Entitlement Inventory Tracker, Cloud Access Audit, SaaS Entitlement Management, IAM Compliance Tracker, Access Rights Audit, Privilege Management Excel, Identity Governance, User Access Review, Cloud Security Checklist, Zero Trust Access