
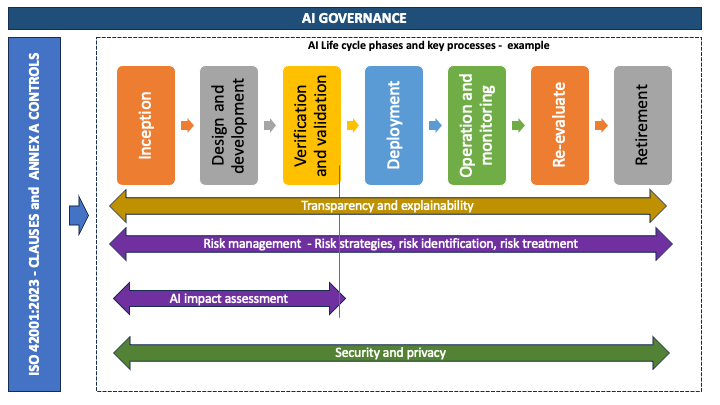
Most organizations think AI risk begins with:
- Breaches
- Prompt injection
- Data leakage
But many AI failures happen without an attacker.
They happen when:
- Models learn from new, unvetted data
- Business context quietly shifts
- Outputs remain “confident” but no longer correct
- Decisions drift away from original intent
This is AI Drift —
and it’s quietly reshaping outcomes across finance, hiring, healthcare, fraud, and operations.
Yet in most enterprises:
- Drift is tracked (sometimes) by data teams
- Discussed as “accuracy degradation”
- Reviewed quarterly… if at all
From a CISO lens, that’s a blind spot.
Because drift changes decisions,
and changed decisions create:
- Regulatory exposure
- Ethical violations
- Financial loss
- Reputational damage
All without a single alert firing.
🧭 The CloudCSF Reframe
AI drift is not just a model performance issue.
It’s a trust failure in slow motion.
Security leaders must start asking:
- 🔍 When did this model last change behavior?
- 🔗 Which business decisions depend on it today?
- 📊 What data is now influencing outcomes?
- 🧾 Who re-approved this AI after it drifted?
If drift isn’t governed,
AI trust expires silently.
✅ Action for Today (CISO Move)
Treat AI drift like you treat:
- Configuration drift
- Access drift
- Policy drift
Require:
- Regular AI behavior reviews
- Re-approval checkpoints
- Decision impact assessments
- Clear stop-or-rollback authority
If AI is allowed to evolve without governance,
it will eventually evolve out of alignment with your risk appetite.
🧩 Closing Thought
Security once focused on keeping bad actors out.
AI security must also focus on
keeping trusted systems trustworthy over time.
CloudCSF exists to help CISOs manage not just AI access —
but AI alignment, accountability, and ongoing trust.
🔖 Hashtags
#CloudCSF #AIDrift #AIGovernance #AISecurity #CISO2_0 #CyberGRC #DigitalTrust #ResponsibleAI #AICompliance #TrustFabric #SecurityLeadership #AITrust
AI Drift,AI Drift Security,AI Governance,AI Security,Cloud AI Security,AI Risk Management,CISO AI Risk,AI Compliance,ISO 42001,NIST AI RMF,CSA AICM,Responsible AI,AI Trust,Digital Trust,CloudCSF,Cyber GRC,AI Audit,Enterprise AI Risk,AI Model Governance,AI Lifecycle Risk,AI Monitoring Governance,AI Risk Framework,CISO 2.0,AI Decision Risk,Trust Fabric,AI Accountability,AI Control Drift