
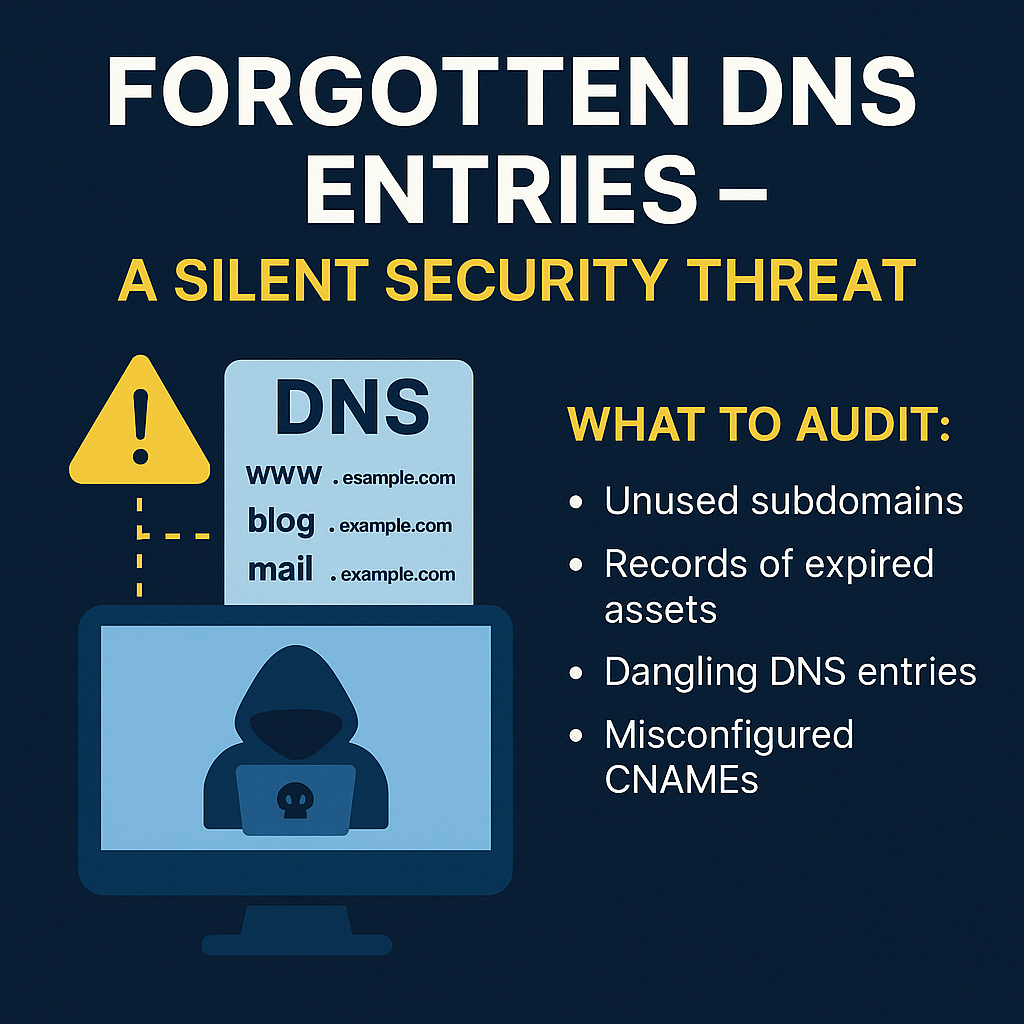
🚨 CloudCSF | Day 33 – Control Spotlight: Forgotten DNS Entries – Exposing Subdomain Hijack Risks!
🧠 Did you know?
Orphaned or outdated DNS records are a silent but deadly risk vector. Attackers often exploit forgotten subdomains to host malicious content, launch phishing attacks, or gain entry via hijacked services.
🔍 What to Audit:
✅ Unused subdomains still pointing to decommissioned services
✅ DNS records tied to expired cloud assets (e.g., unlinked S3 buckets, Heroku, Azure apps)
✅ CNAME entries without proper TTL or verification
✅ Third-party services with dangling DNS (e.g., GitHub Pages, Netlify, Vercel)
🔒 Why This Matters:
Subdomain hijacking isn’t just theoretical—it’s been used in real-world breaches to:
- Steal user data
- Trick internal employees
- Bypass email filters and brand protections
🛠️ How to Fix It:
- Run automated scans for stale DNS records weekly
- Monitor DNS zones for dangling records with CSPM tools
- Create an internal decommission checklist that includes DNS validation
- Use tools like
dnsrecon,Amass, orSubjackto identify risks proactively - Remove or update misconfigured entries immediately
✅ Pro Tip:
Make DNS hygiene part of every DevSecOps pipeline. Treat DNS like source code – review, update, and secure it continuously.
📥 Download:
Want a ready-to-use “Forgotten DNS Risk Tracker” (Excel + PDF)?
✅ Comment “DNS” and we’ll DM it to you instantly!
🔁 Like | Share | Tag a DevOps Leader or DNS Owner who should read this today!
#CloudCSF #CybersecurityAwareness #DNSAudit #SubdomainHijacking #CloudSecurity #DevSecOps #CyberRisk #CloudInfraHygiene #CISORadar #DigitalTrust #InfosecTips