
🔐 CloudCSF – Day 35
🎯 “Third-Party Integrations: The Trojan Horses of SaaS?”
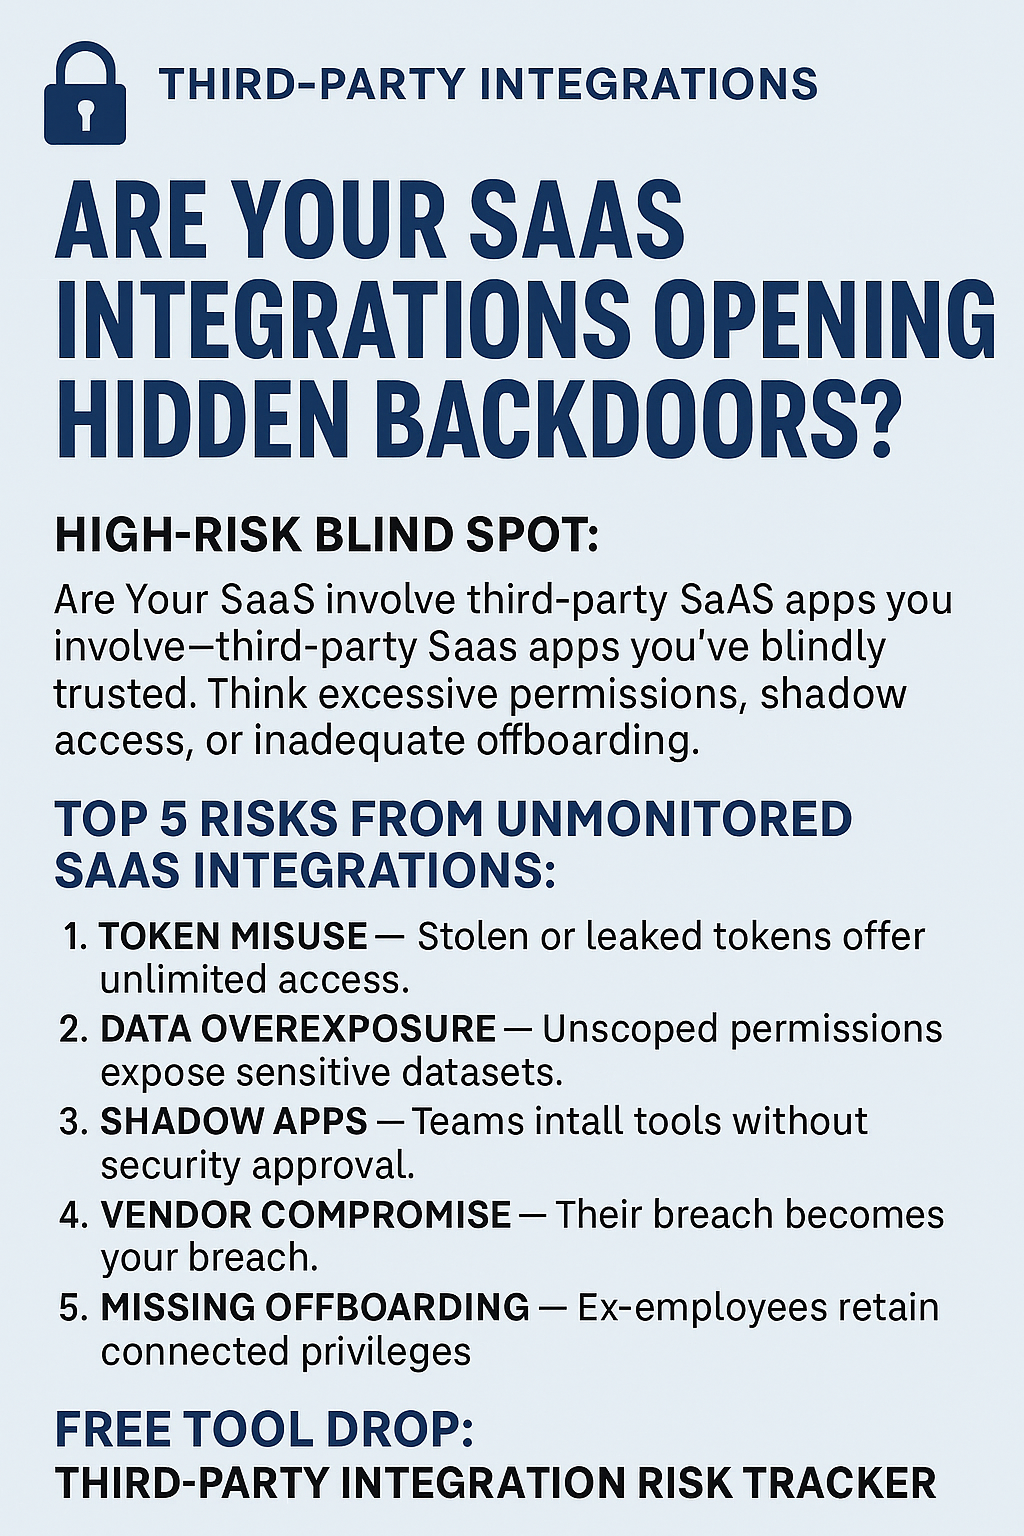
🛡️ Post Title: Are Your SaaS Integrations Opening Hidden Backdoors?
🚨 High-Risk Blind Spot:
Your most secure cloud environment can be exposed—not from within, but through a connected third-party SaaS app you’ve blindly trusted. Think CRMs, billing tools, marketing plugins. Each one may have excessive permissions, shadow access, or inadequate offboarding.
🧠 High-Value Insight:
🔸 63% of SaaS breaches now involve third-party integrations.
🔸 OAuth tokens and API keys are often never rotated.
🔸 Visibility into these apps is poor to non-existent in many orgs.
📉 Top 5 Risks from Unmonitored SaaS Integrations:
- Token Misuse — Stolen or leaked tokens offer unlimited access.
- Data Overexposure — Unscoped permissions expose sensitive datasets.
- Shadow Apps — Teams install tools without security approval.
- Vendor Compromise — Their breach becomes your breach.
- Missing Offboarding — Ex-employees retain connected privileges.
📥 Free Tool Drop:
🚀 Download our Third-Party Integration Risk Tracker (Excel + PDF)
✅ Score SaaS risks by data sensitivity, vendor maturity, token hygiene, breach exposure
✅ Track integration inventory, revoke unnecessary access, set review cycles
🔗 [Link to Download]
🧭 CloudCSF Goal:
“Empower security leaders to turn blind integration zones into zero-trust gateways.”
🔁 Repost if you’re auditing integrations.
💬 Comment if you’d like a walkthrough session.
#CloudCSF #Day35 #SaaSSecurity #ThirdPartyRisk #OAuthSecurity #APISecurity #SaaSIntegrations #ShadowIT #ZeroTrust #CyberGRC #AuditSecIntel #DigitalTrustByDesign
third-party saas risk,saas integration security,cloud app security,saas risk management,third-party vendor risks,cloud integration audit,saas token misuse,shadow saas risks,data overexposure,cybersecurity audit templates,saas security checklist,cloud security governance,saas offboarding risks,cloud compliance,identity access management
Disclaimer: This post provides general information and is not tailored to any specific individual or entity. It includes only publicly available information for general awareness purposes. Do not warrant that this post is free from errors or omissions. Views are personal