
🌩️ CloudCSF – Day 22
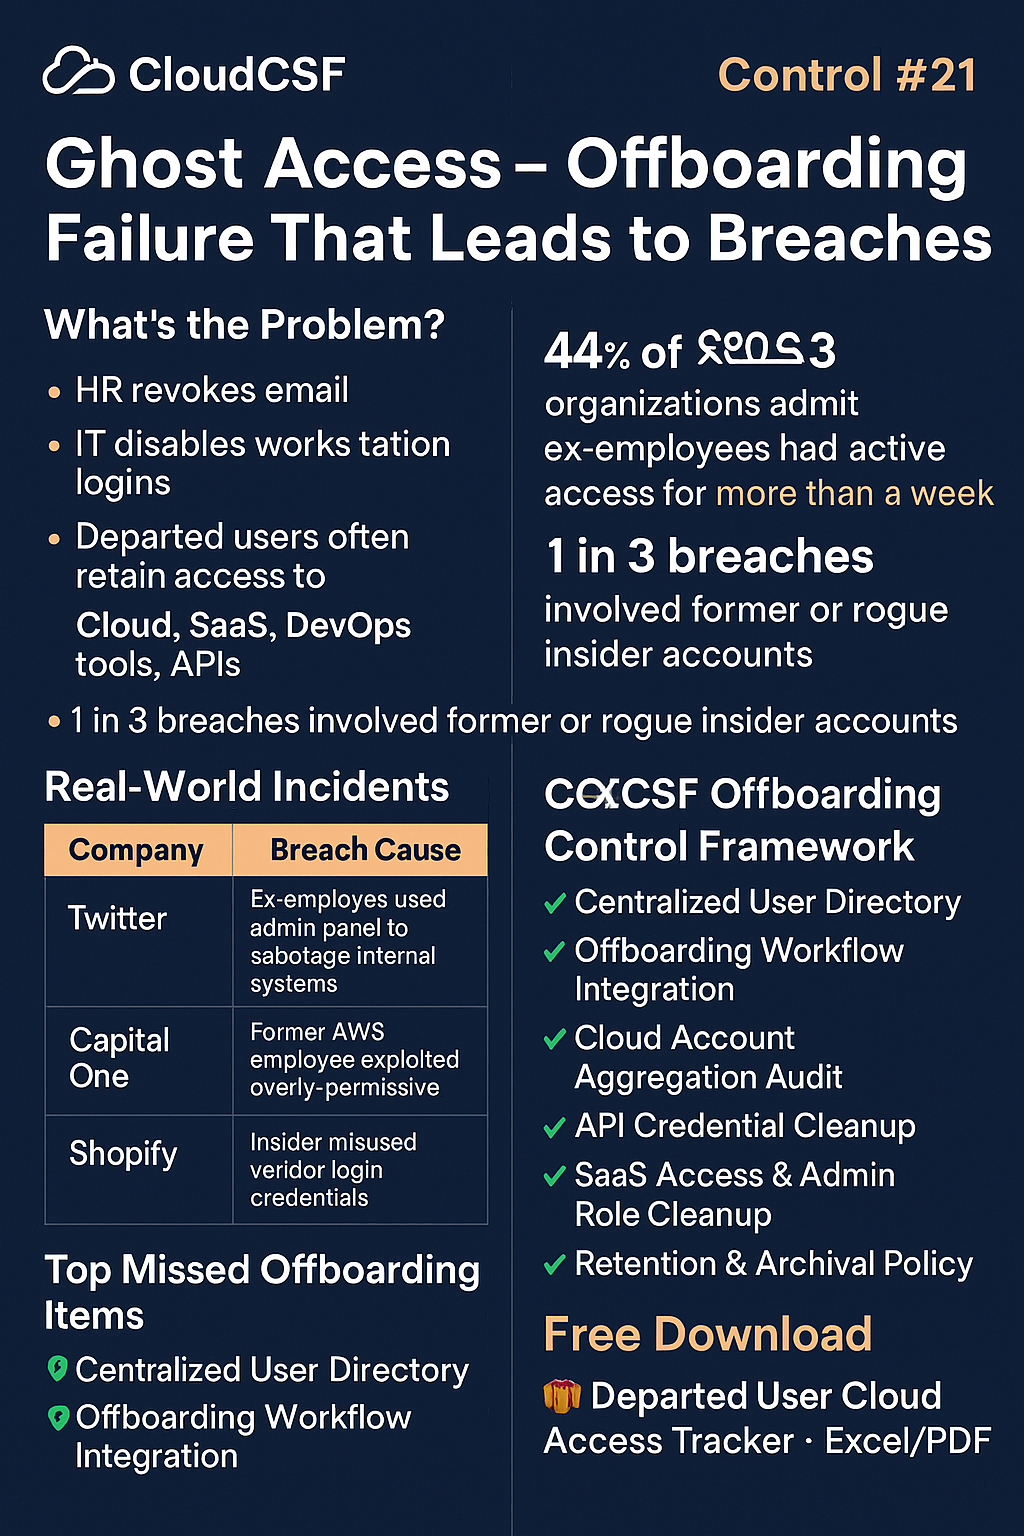
Control #21: Ghost Access – Offboarding Failure That Leads to Breaches
“You revoked their email. But did you revoke their AWS, GitHub, Zoom, and 10 other apps?”
🔍 What’s the Problem?
Most organizations assume user offboarding is complete once:
- HR revokes email
- IT disables workstation logins
But in reality:
- Departed users often retain access to Cloud, SaaS, DevOps tools, and APIs
- 44% of organizations admit ex-employees had active access for more than a week
- 1 in 3 breaches involved former or rogue insider accounts
🧠 Real-World Incidents
| Company | Breach Cause |
|---|---|
| Ex-employee used admin panel to sabotage internal systems | |
| Capital One | Former AWS employee exploited overly-permissive roles |
| Shopify | Insider misused vendor login credentials |
🚨 Top Missed Offboarding Items
- ✅ GitHub/GitLab account not revoked
- ✅ Cloud accounts (AWS, Azure, GCP) still active
- ✅ Slack/Zoom/CRM access not terminated
- ✅ SSO/IdP not de-provisioned across all apps
- ✅ API keys & secrets owned by former devs still valid
- ✅ Shared mailbox or Google Drive not locked
🔐 CloudCSF Offboarding Control Framework
- Centralized User Directory
- Use Azure AD / Okta / JumpCloud
- Automate app access provisioning & deprovisioning
- Offboarding Workflow Integration
- Tie offboarding to HRMS like SAP, Workday, Zoho People
- Trigger checklist-based access revocation
- Cloud Account Aggregation Audit
- Periodically review accounts in AWS IAM, GCP IAM, Azure AD
- Detect accounts not linked to HR records
- API Credential Cleanup
- Scan and revoke lingering tokens tied to ex-users
- Rotate service account credentials if needed
- SaaS Access & Admin Role Cleanup
- Remove admin rights from Zoom, M365, Notion, CRM tools
- Use SSPM / CASB to monitor all accounts post-termination
- Retention & Archival Policy
- Ensure former user’s data is archived, encrypted, or deleted per policy
🧰 Tools You Can Use
- 🧩 Offboarding Automation: Okta Workflows, BetterCloud, Torii
- 🔎 Cloud IAM Audit: AWS IAM Access Analyzer, Azure Entitlement Mgmt
- 🛠️ CASB/SSPM: DoControl, AppOmni, Netskope
- ✅ DevOps Access Scanning: GitHub Token Audit, GitLeaks
🧪 Maturity Model
| Maturity Level | Characteristics |
|---|---|
| 🚫 Level 0 | Manual offboarding, no audit |
| ⚠️ Level 1 | Ad-hoc deactivation, inconsistent logs |
| 🔐 Level 2 | Semi-automated, checklist-based revocation |
| 🧠 Level 3 | Centralized directory & SSO enforcement |
| 🧬 Level 4 | Continuous validation, auto-revocation, alerts |
📄 Free Download
🎁 Departed User Cloud Access Tracker – Excel/PDF
A 2-in-1 template to track offboarding across cloud, SaaS, DevOps, and user identity sources.
🔁 Tomorrow’s Post:
Day 23 – Control #22: Cloud Workloads with Public IPs – When Internal Becomes Internet-Facing
Employee Offboarding Checklist, Cloud Access Audit, Former Employee Data Breach, SaaS Offboarding Workflow, Cloud Identity Governance, Ghost Access Risk, Deprovisioning Cloud Accounts, IAM Security Best Practices, API Token Cleanup, Cloud Account Termination Audit