
🌐 CloudCSF Day 21
Control #20: SaaS Misconfigurations – Where Convenience Meets Compromise
“Your CRM, HRMS, or file-sharing app might already be leaking more than you think.”
🧠 Why SaaS Misconfigurations Are a Major Security Blindspot
Organizations use dozens (sometimes hundreds) of SaaS apps:
Salesforce, Zoom, Microsoft 365, Dropbox, Slack, Notion, Google Workspace…
🔍 But how many of these apps are:
- Exposing sensitive data through public links?
- Lacking MFA?
- Giving ex-employees full admin access?
- Connected to unmonitored third-party apps?
Misconfigurations in SaaS settings can silently expose:
- Customer data (CRM)
- Internal files (Google Drive, Dropbox)
- Business secrets (Slack, Notion)
- Identity & tokens (OAuth scopes)
🧨 Real-World SaaS Misconfiguration Incidents
| Company | Incident |
|---|---|
| Accenture | Misconfigured Box folder leaked internal documents |
| GitHub | Publicly indexed Gist files with secrets |
| 540M user records exposed via third-party SaaS app |
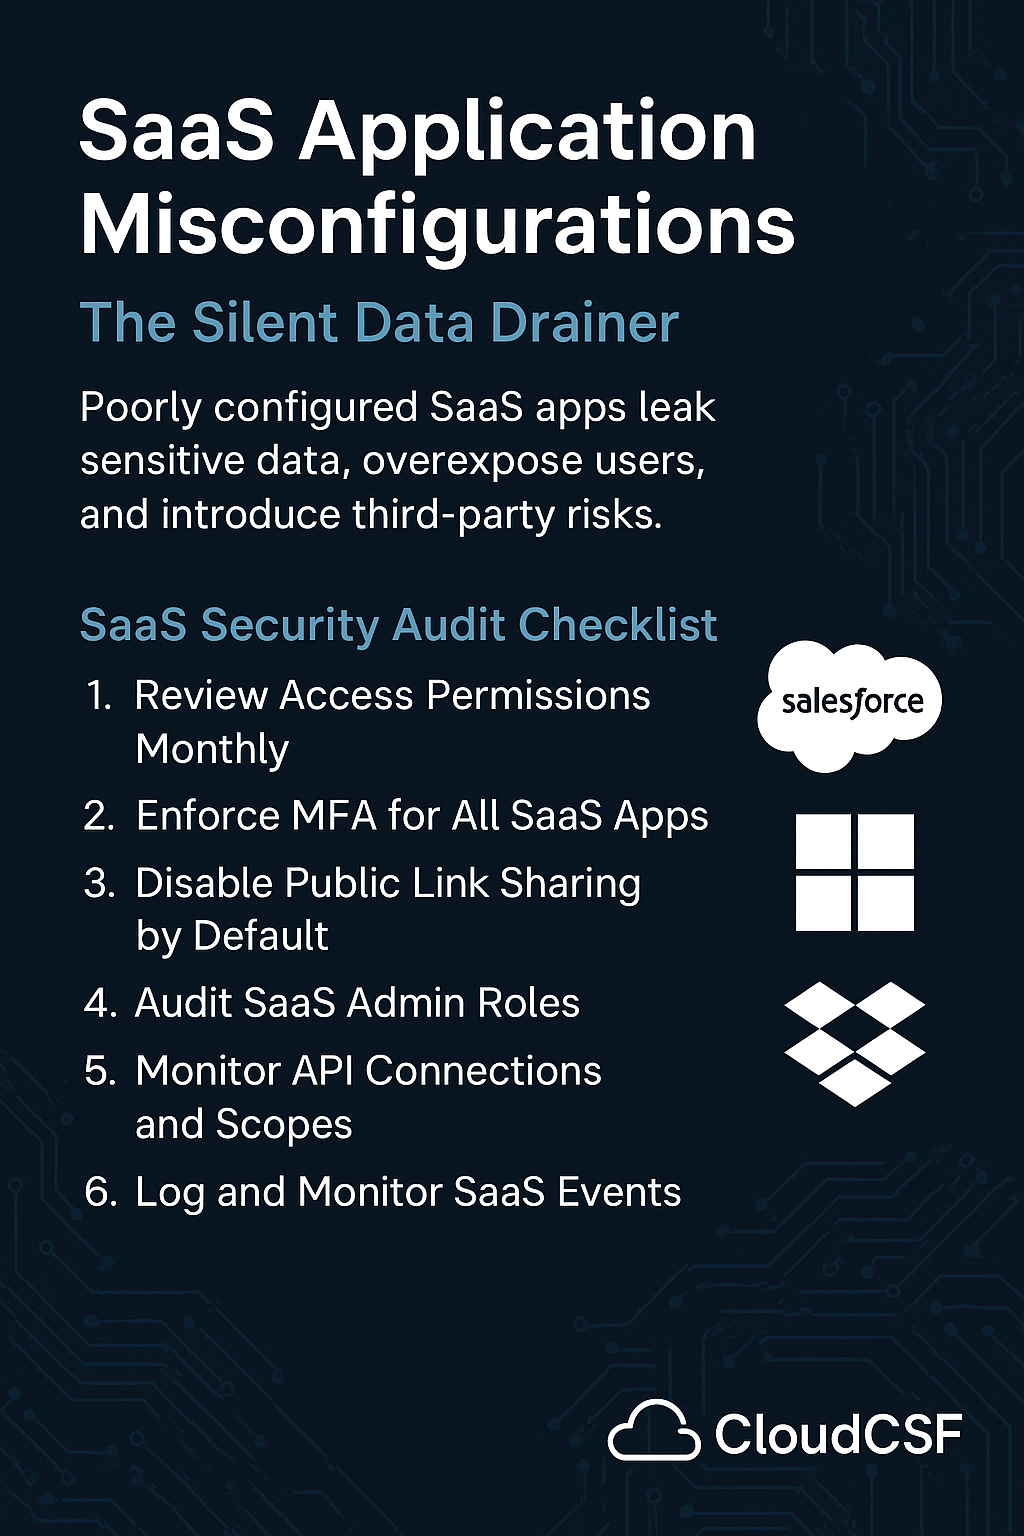
✅ CloudCSF SaaS Security Audit Checklist
- Review Access Permissions Monthly
- Especially for ex-employees and vendors
- Audit OAuth-connected apps
- Enforce MFA for All SaaS Apps
- Especially business-critical (email, file storage, finance)
- Use IdP integration for centralized control
- Disable Public Link Sharing by Default
- Google Drive, Dropbox, Notion, SharePoint
- Monitor shared link access logs
- Audit SaaS Admin Roles
- No single admin; use least privilege
- Monitor role changes and access logs
- Monitor API Connections and Scopes
- Look for over-scoped tokens
- Rotate and revoke stale integrations
- Log and Monitor SaaS Events
- Use CASB / SaaS Security Posture Management (SSPM)
- Detect unusual logins, downloads, or permission changes
🧪 SaaS Security Maturity Levels
| Level | Description |
|---|---|
| ❌ 0 – Ad-hoc use with no governance | Shadow IT risk |
| ⚠️ 1 – MFA enabled but no audits | Limited control |
| 🔐 2 – Role & permission audits + API visibility | Moderate security |
| 🧠 3 – Centralized SSO & SSPM tooling | Strong governance |
| 🧬 4 – Continuous monitoring & automated remediation | Advanced resilience |
🛠 Tools to Help
- 🔐 SSPM Tools: AppOmni, Obsidian, DoControl
- 🔎 CASB: Netskope, Microsoft Defender for Cloud Apps
- 📊 IdP Logs: Okta, Azure AD, Google Workspace
📥 Bonus Download
📄 [SaaS App Security Audit Template – PDF]
✔️ Checklist covering user access, MFA, link sharing, third-party apps, and misconfig risk scoring.
💬 Comment
Which SaaS app do you trust the least with sensitive data?
👇 Comment “Not So SaaSy 🧩” to get the free audit template.
🔁 Coming Tomorrow:
Day 22: Control #21 – Cloud Misuse by Departed Employees