
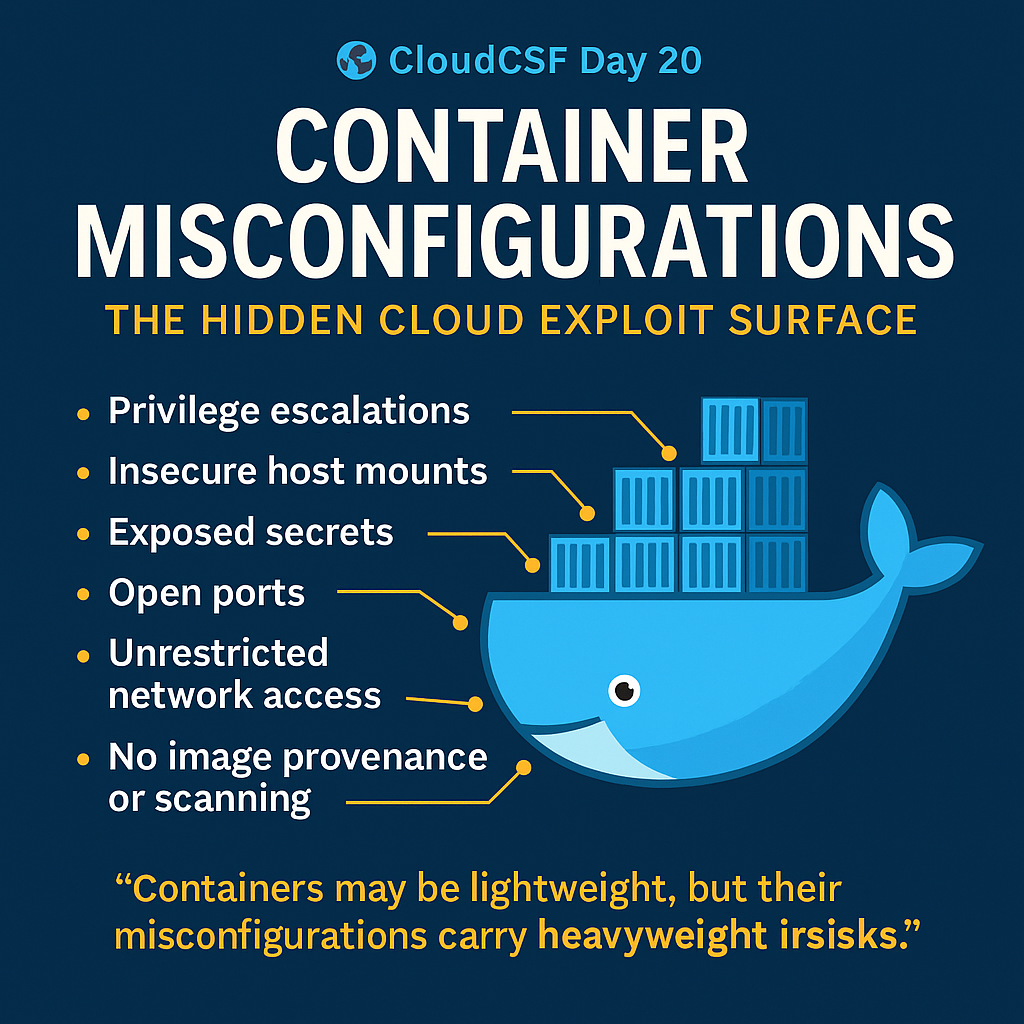
🌐 CloudCSF Day 20
Control #19: Container Misconfigurations – The Hidden Cloud Exploit Surface
“Containers may be lightweight, but their misconfigurations carry heavyweight risks.”
🧠 Why Container Misconfigs Are a Cloud Breach Goldmine
Modern cloud-native apps heavily rely on Docker, Kubernetes, and containers — but misconfigured containers often introduce:
- 🔓 Privilege escalations
- 📂 Insecure host mounts
- 🧬 Exposed secrets
- 🌐 Open ports
- 🔁 Unrestricted network access
- 🛠️ No image provenance or scanning
🚨 Famous Container-Based Breaches
| Company | Breach Vector |
|---|---|
| Tesla | Kubernetes dashboard exposed, used for crypto mining |
| Shopify | Misconfigured Docker used to escalate privileges |
| Capital One | SSRF to metadata endpoint → privilege escalation in containers |
✅ CloudCSF Container Audit Checklist
- Use Minimal Base Images
- Alpine, Distroless, or custom hardened images
- Avoid full OS images unless required
- Avoid Running as Root
- Use
USERdirective in Dockerfiles - Enforce non-root containers in K8s policies
- Use
- Remove Secrets from Images
- Never embed credentials or tokens
- Use secret mounts or env injection via orchestrators
- Scan Images Automatically
- Integrate tools like Trivy, Clair, Aqua, Snyk
- Shift left scanning in CI/CD
- Limit Host Access
- Avoid hostPath volumes unless necessary
- Drop all Linux capabilities not needed
- Restrict Container Networking
- Use Network Policies in K8s
- Block cross-container talk unless required
- Enable Runtime Protection
- Use tools like Falco, Sysdig, or eBPF-based agents
🧪 CloudCSF Maturity Snapshot
| Maturity Level | Status |
|---|---|
| ❌ 0 – Default Docker with root | High risk |
| ⚠️ 1 – Basic hardening | Still vulnerable |
| 🔒 2 – Policy + scanning enabled | Reasonable security |
| 🧠 3 – Runtime protection + compliance | Strong control |
| 🧬 4 – GitOps + Automated remediations | Advanced resilience |
🛠 Tools to Use
- 🔍 Trivy, Snyk, Clair – Image scanners
- 🔐 OPA Gatekeeper, Kyverno – Kubernetes policies
- 🔎 Falco, Sysdig – Runtime anomaly detection
- ⚙️ Dockle, DockerSlim – Image optimization/hardening
📥 Bonus Download
📄 [Container Misconfiguration Risk Tracker – PDF]
✔️ Use this to assess 20+ config items across build, deploy, and runtime.
💬 Comment Prompt:
How often do you scan your containers before deployment?
👇 Comment “Scan It Before You Ship It 📦” to get the PDF instantly.
🔁 Coming Tomorrow:
Day 21: Control #20 – SaaS Application Security Misconfigurations