
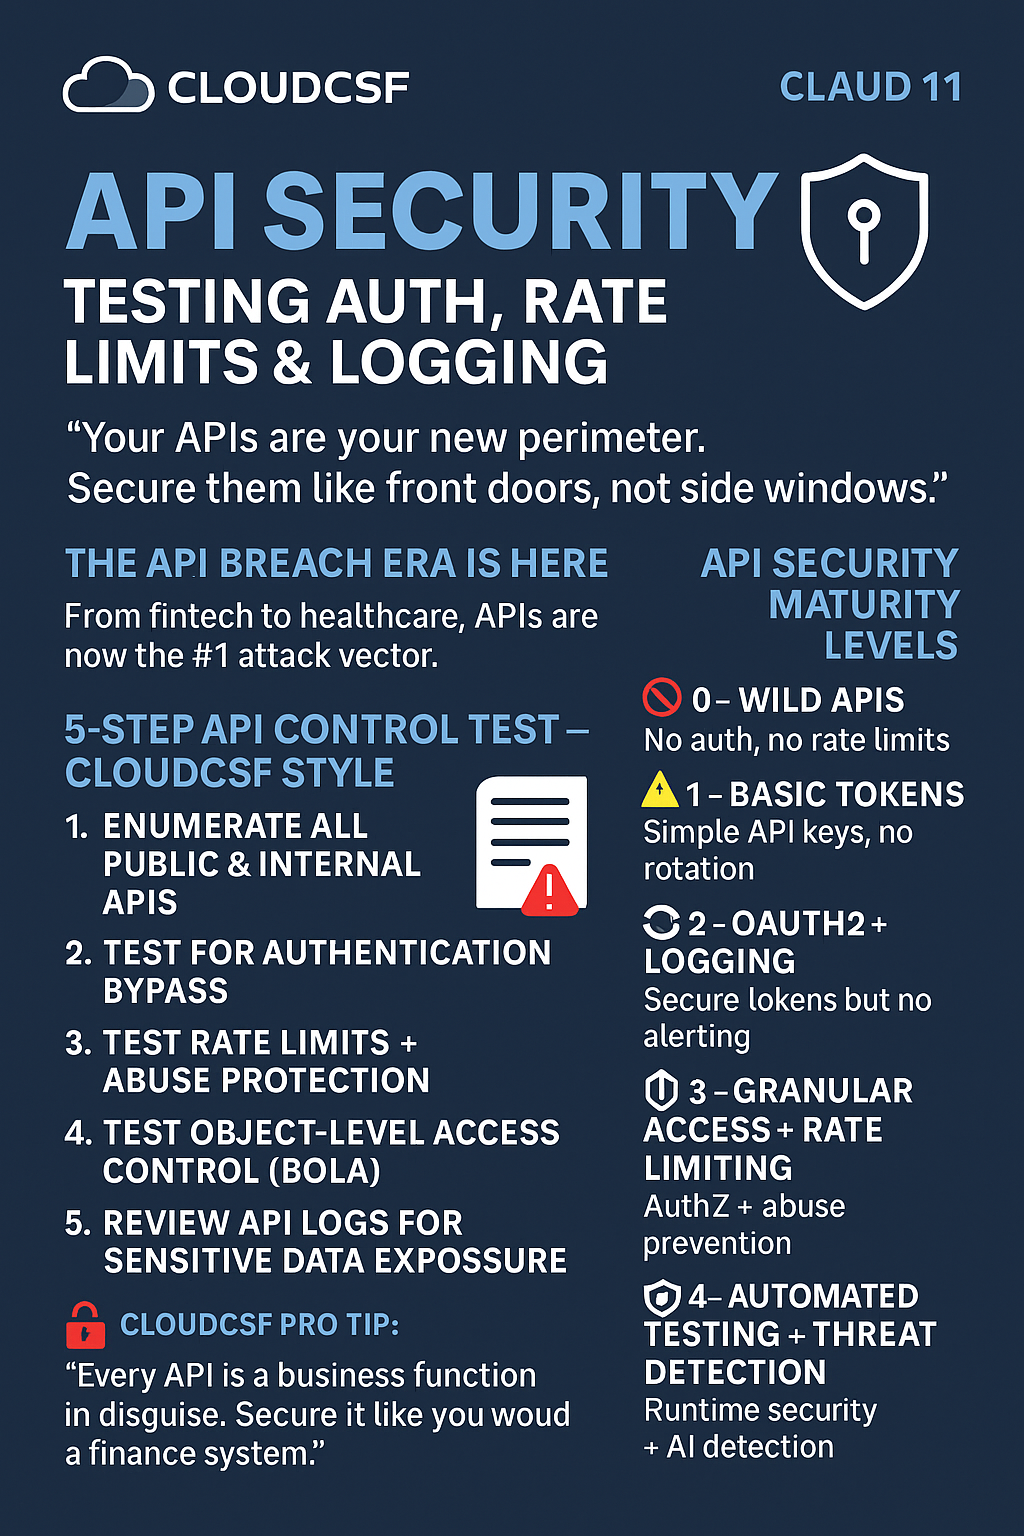
🎯 Goal: Help organizations secure APIs by testing the most exploited weaknesses: authentication, abuse protection, and observability.
🔐 CloudCSF Day 11
Control #10: API Security – Testing Auth, Rate Limits & Logging
“Your APIs are your new perimeter. Secure them like front doors, not side windows.”
🚨 The API Breach Era Is Here
From fintech to healthcare, APIs are now the #1 attack vector — and often the least tested part of cloud security.
Real-world examples:
- 🔓 A public API leaked PII because authentication was missing
- 🧨 A rate-limiting bypass allowed mass credential stuffing
- 📭 APIs exposed sensitive fields because logging wasn’t filtered
- 🛑 Broken object-level access let users pull other users’ data
APIs power your business. They can also expose it.
🔍 What Is API Security Testing?
This control validates that APIs:
- Enforce strong authentication (OAuth2, JWT, mutual TLS)
- Have rate limits and abuse protection
- Properly authorize every user per action and object
- Log and alert on abnormal patterns
- Filter out sensitive data from logs and error messages
✅ 5-Step API Control Test – CloudCSF Style
- Enumerate All Public & Internal APIs
- Check Swagger/OpenAPI docs, Postman collections, traffic logs
- Include mobile app APIs and integrations
- Test for Authentication Bypass
- Try to hit endpoints without tokens
- Try expired/forged tokens and observe behavior
- Test Rate Limits + Abuse Protection
- Use tools like OWASP ZAP, Burp Suite, Postman Runner
- Try 100+ calls in seconds — was it throttled?
- Test Object-Level Access Control (BOLA)
- Can user A fetch user B’s data using another ID?
- Manually manipulate IDs in the request path
- Review API Logs for Sensitive Data Exposure
- Are tokens, PII, passwords, keys logged?
- Are failed access attempts monitored and alerted?
📊 API Security Maturity Levels
| Level | Description |
|---|---|
| 🚫 0 – Wild APIs | No auth, no rate limits |
| ⚠️ 1 – Basic Tokens | Simple API keys, no rotation |
| 🔁 2 – OAuth2 + Logging | Secure tokens but no alerting |
| 🔐 3 – Granular Access + Rate Limiting | AuthZ + abuse prevention |
| 🛡️ 4 – Automated Testing + Threat Detection | Runtime security + AI detection |
🛠️ Tools You Can Use
- ✅ OWASP ZAP, Postman, Burp Suite
- ✅ 42Crunch, APIsec, Salt Security, Traceable AI
- ✅ GCP Apigee, AWS API Gateway, Azure API Management
- ✅ CloudTrail logs, API Gateway logs, WAF logs
- ✅ CI/CD hooks for OpenAPI linting + scanning
💡 CloudCSF Pro Tip
“Every API is a business function in disguise. Secure it like you would a finance system.”
🎁 Free Resource
👉 [Download the API Security Audit Checklist (PDF)]
👉 Join the CloudCSF WhatsApp Group for templates and tools
💬 Comment :
Have you ever tested your APIs for BOLA or rate limit abuse?
Drop “API 🔐” and we’ll send you the full checklist.
🔁 Coming Tomorrow:
Day 12: Control #11 – Threat Modeling: Aligning Controls with Real Risks