
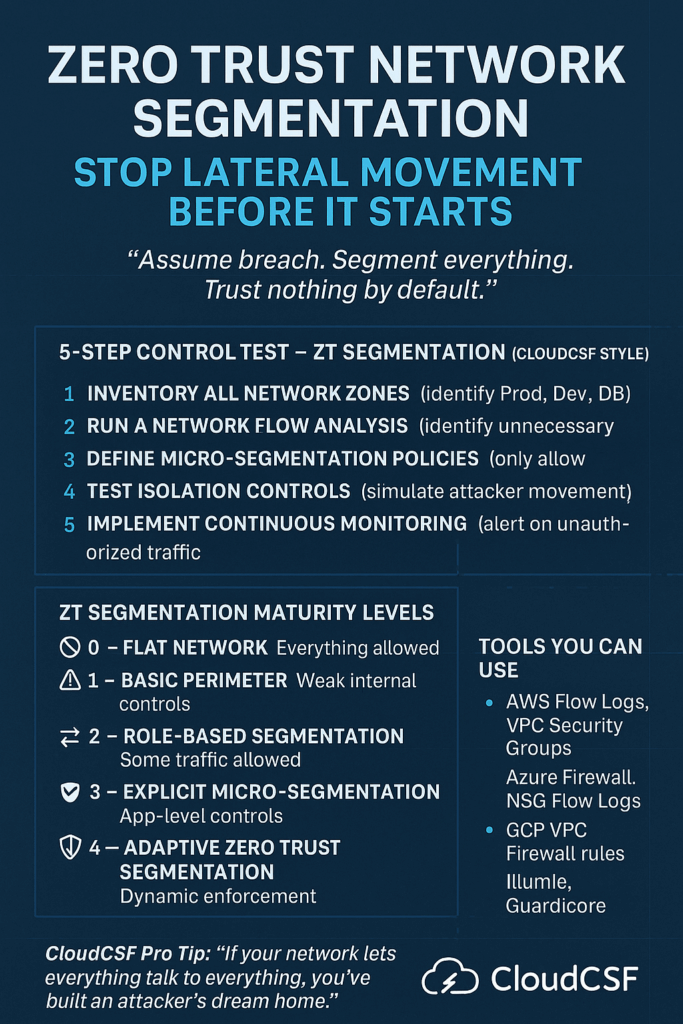
🎯 Goal: Help organizations test and implement Zero Trust network controls to isolate, protect, and limit internal attack spread.
🔐 CloudCSF Day 8
Control #7: Zero Trust Network Segmentation – Stop Lateral Movement Before It Starts
“Assume breach. Segment everything. Trust nothing by default.”
🧨 The Internal Movement That Wrecks Organizations
In almost every major breach, initial access wasn’t the worst part —
It was the lateral movement that followed.
🚨 A developer account gets phished.
➡️ That account had access to a shared network zone.
➡️ The attacker hops from logs → databases → backups → entire infrastructure.
✅ Why? No segmentation. All internal systems trusted each other.
🔍 What Is Zero Trust Network Segmentation?
Zero Trust Segmentation (ZTS) means:
- No system or user is trusted by default
- Workloads and users are isolated by function, need, and behavior
- Communication between zones is explicitly allowed, not implied
- You assume internal compromise is inevitable, and act accordingly
✅ 5-Step Control Test – ZT Segmentation (CloudCSF Style)
- Inventory All Network Zones
- Identify Prod, Dev, DB, Logging, Internet-facing zones
- List which systems talk to which (actual vs. intended)
- Run a Network Flow Analysis
- Tools: AWS VPC Flow Logs, Azure NSG Flow Logs, GCP VPC Logs
- Identify unnecessary east-west traffic
- Define Micro-Segmentation Policies
- Block all inter-zone communication by default
- Only allow via explicit security groups / NSGs / firewall rules
- Test Isolation Controls
- Try to ping or access resources across zones (simulate attacker movement)
- Review logs: are violations logged and alerted?
- Implement Continuous Monitoring
- Use behavior-based alerts
- Auto-disable unauthorized lateral access attempts
📊 ZT Segmentation Maturity Levels
| Level | Description |
|---|---|
| 🚫 0 – Flat Network | Everything talks to everything |
| ⚠️ 1 – Basic Perimeter | Zones exist but allow internal trust |
| 🔁 2 – Role-Based Segmentation | Some groups isolated (e.g., DB) |
| 🔐 3 – Explicit Micro-Segmentation | App-based traffic control |
| 🛡️ 4 – Adaptive Zero Trust Segmentation | Real-time enforcement + anomaly detection |
🛠️ Tools You Can Use
- ✅ AWS VPC Security Groups + Flow Logs
- ✅ Azure Firewall, NSG, Azure Policy
- ✅ GCP VPC Firewalls, IAM + Logs
- ✅ Illumio, Guardicore, Prisma Cloud, Akamai ZTS
- ✅ Zeek, Suricata, Calico (Kubernetes network policies)
💡 CloudCSF Pro Tip
“If your network lets everything talk to everything, you’ve built an attacker’s dream home.”
🎁 Free Resource
👉 [Download the ZT Segmentation Audit Guide (PDF)]
👉 Join the CloudCSF WhatsApp Group to receive daily maturity controls
💬 Comment and Share :
Does your network stop lateral movement before it starts?
Drop “ZeroTrust 🔐” to get the segmentation audit kit.
🔁 Coming Tomorrow:
Day 9: Control #8 – Logging & Monitoring Controls That Actually Work
We’ll test visibility across cloud layers — and separate signal from noise.
Disclaimer: This post provides general information and is not tailored to any specific individual or entity. It includes only publicly available information for general informational purposes. Do not warrant that this post is free from errors or omissions.