
🎯 Goal: Help organizations detect threats faster by ensuring logging, retention, and actionable monitoring are in place across the stack.
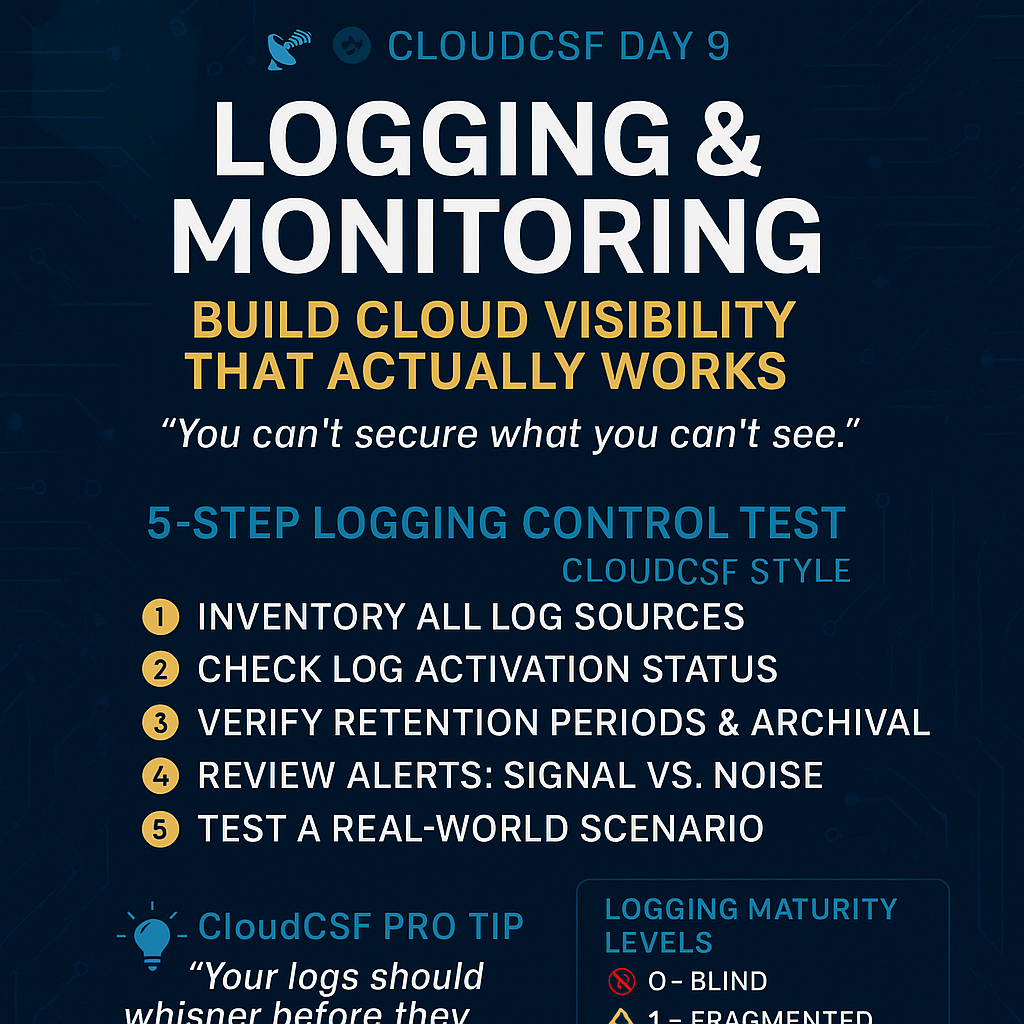
🛰️ CloudCSF Day 9
Control #8: Logging & Monitoring – Build Cloud Visibility That Actually Works
“You can’t secure what you can’t see.”
🔍 The Reality of “Blind Spots” in the Cloud
Organizations think they are “monitoring everything” — but here’s what’s really happening:
- ✅ CloudTrail is enabled… but only logs write events, not read access
- ❌ S3 access logs are off — attackers download data unnoticed
- 🚫 GCP audit logs only track Admin activity, missing data plane actions
- ⏳ Logs are stored for 7 days — but your detection team reviews every 15
👉 The result? Delayed detection, failed compliance, and invisible breaches.
🎯 What Is Cloud Logging & Monitoring?
This control ensures:
- All critical activities are logged centrally
- Logs are retained based on policy (90+ days recommended)
- Real-time or near-real-time monitoring and alerting is active
- Noise is filtered — so alerts are meaningful and actionable
✅ 5-Step Logging Control Test – CloudCSF Style
- Inventory All Log Sources
- IAM activity, storage access, VPC flow logs, DB queries, firewall events
- Include SaaS services (O365, Salesforce, GitHub, etc.)
- Check Log Activation Status
- Are logs enabled? Which types: management, data, event, access?
- Do they cover ALL regions and services?
- Verify Retention Periods & Archival
- Are logs retained for >90 days?
- Do you archive to immutable storage (e.g., S3 with versioning & MFA delete)?
- Review Alerts: Signal vs. Noise
- Are high-severity events lost in alert storms?
- Is the SOC missing critical anomalies?
- Test a Real-World Scenario
- Simulate a data exfil or policy change
- Measure: Was it logged? Was it alerted? Was it acted upon?
📊 Logging Maturity Levels
| Level | Description |
|---|---|
| 🚫 0 – Blind | Logging disabled or partial |
| ⚠️ 1 – Fragmented | Logs stored locally or not centralized |
| 🔁 2 – Centralized | Logs in SIEM/SOC, but unfiltered |
| 🔐 3 – Tuned & Actionable | Correlated + prioritized alerts |
| 🛡️ 4 – Automated Response | SOAR + AI-based triage activated |
🛠️ Tools You Can Use
- ✅ AWS CloudTrail, CloudWatch Logs, GuardDuty
- ✅ Azure Monitor, Sentinel, Log Analytics
- ✅ GCP Cloud Logging, Security Command Center
- ✅ ELK Stack, Datadog, Splunk, Wazuh, Panther
- ✅ SOAR Platforms: XSOAR, Tines, Siemplify
💡 CloudCSF Pro Tip
“Your logs should whisper before they scream. Tune them before you trust them.”
🎁 Free Resource
👉 [Download: Logging & Monitoring Readiness Checklist (PDF)]
👉 Join the CloudCSF WhatsApp Group for templates, daily insights, and tools
💬 Comment :
How confident are you that your cloud logs will catch your next breach?
Comment “Logs 📡” to receive the readiness checklist.
🔁 Coming Tomorrow:
Day 10: Control #9 – Public Exposure Test: Can Your Org Be Found from Google?
We’ll run real-world recon to find weak links — before hackers do.